

Think of generative AI, short for generative artificial intelligence, as a very quick digital artist. It writes text. It makes images. It can even put together ideas without anyone holding its hand, all by soaking up huge amounts of material it has seen before and producing something new from it. So why should security people care? Because not long ago, most cyber threats were puzzles you could crack with a bit of patience. Generative AI changed the difficulty level. Attackers now have smarter tools too, and the attacks they build with them hit harder and are harder to spot.
Cybersecurity has one job: keep our digital lives safe. Generative AI shows up on both sides of that fight, as a sword and as a shield. Defenders get new ways to spot and block intrusions. But here’s the catch. The same technology hands criminals a way to make their attacks quieter and more dangerous.
Below, we’ll walk through why generative AI matters for cybersecurity and what you actually gain from it. Let’s get into it.
Knowing the Effects Of Generative AI
“Generative AI” is the branch of machine learning where models learn from input data and then produce new data with the same features and patterns. That simple trick opens a lot of doors: better problem-solving, new creative work, faster content production. McKinsey estimates generative AI could add trillions of dollars a year to the global economy.
There’s a flip side. Generative AI eats data, lots of it, so businesses have to think hard about security and privacy. Large language models (LLMs) and other Generative AI models raise privacy problems simply because of how they work: they memorize and they associate. An LLM can hold on to chunks of its training data, sensitive details included, and those details can later be pulled out or leaked.
Role of Generative AI in Cybersecurity
So where does generative AI actually show up in security? Start with how attackers use it:
- Creating Phishing Emails: Criminals can use GenAI to write phishing emails that read like the real thing, convincing enough that people click the bad link or hand over personal details.
- Making Fake Websites: Generative AI makes it easy to spin up fake websites that look legitimate. Visitors get fooled into downloading malware or typing in information they shouldn’t.
- Creating Malicious Code: Attackers can also have generative AI write code aimed squarely at security holes in computer systems.
That’s the bad news. Generative AI in security has upsides and downsides, and on the downside, it can produce elaborate attacks that are genuinely hard to stop.
The good news? Defenders get new approaches out of the same technology. Used well, they make attacks easier to catch and easier to prevent.
The Working of Generative AI
Generative AI grows out of machine learning (ML), which is itself a slice of AI. ML algorithms improve on their own by finding patterns in enormous piles of data. One branch of ML, deep learning, stacks algorithms in layers called neural networks, loosely modeled on how neurons fire in the human brain. That structure is what lets a system learn and make decisions by itself.
Inside deep learning, there’s a specific neural network design called the transformer. A transformer processes incoming data in parallel through layers of artificial neurons, which makes it very efficient. The best known of these is the Generative Pre-Trained Transformer, or GPT.
Boiled down, generative AI works in three steps:
- First, the model trains on a massive dataset.
- Next, it picks up the underlying structures and patterns in that data.
- Finally, it generates new data that follows those same structures and patterns.
Read Also: Agentic AI in Cybersecurity
Benefits and Drawbacks of Generative AI in Cybersecurity
Generative AI in cybersecurity brings real advantages, and it answers a good number of the headaches security professionals deal with today.
- Efficiency: GenAI can make detecting and responding to threats a lot faster. An AI-native system keeps learning, and as it does, it helps analysts find the information they need to make a call quickly. Their work moves faster, they get time back for other projects, and the whole team gets more done.
- Comprehensive Analysis and Summarization: Teams can use GenAI to sift data from many modules and sources, doing quickly and accurately the slow, tedious analysis that used to be done by hand. It can also write plain-language summaries of incidents and threat assessments, which multiplies what a team can produce.
- Proactive Threat Detection: The biggest win is probably this one: moving security from reactive to proactive. GenAI learns patterns and flags likely risks early, so teams can act before a breach instead of cleaning up after one.
None of this comes free. AI-based security has plenty of uses, but it also has real problems, and like any technology it needs careful handling to keep risk and abuse in check.
- High Processing Resources: Training GenAI models takes serious computing power and storage. For smaller businesses, that alone can put it out of reach.
- Threat of Attackers Using AI: GenAI models and tools keep getting easier to get hold of, thanks to open-source, cheap, cloud-based options. Companies use them for defense. Criminals use them too, building sophisticated attacks designed to slip past security controls. With a growing set of GPT-based tools out there, even brand-new threat actors can pull off attacks that once took real expertise.
- Ethical Issues: There’s also an ongoing debate about ethics, mostly around privacy and who controls data, and especially about what kinds of data end up in AI training sets.
Read Blog: Generative AI Use Cases
How Generative AI Enhances Cybersecurity?
Here’s how Gen AI is helping security teams protect their organizations with more precision and less wasted effort.
1. Assisting Security Units That are Understaffed
Most security teams are stretched thin. AI is being brought in to back them up and get better results. The vast majority of IT leaders (93%) are either exploring AI and ML for security or already using them [SOURCE NEEDED]. The early adopters are seeing gains already: fewer false positives, less noise, better detection of zero-day attacks and threats, and sharper prioritization of Tier 1 threats. Encouraged by those early signs, more than half of managers (52%) think generative AI security will help their organizations put people, resources, capacity and skills where they count [SOURCE NEEDED].
2. Real-time Threat Detection
Threat detection is one of the most common ways generative AI gets used right now. It filters event alerts more effectively, throws out false positives and picks up trends and anomalies fast. Put together, that lets an organization spot new threat vectors much sooner than it could before.
3. Improving the Quality of Threat Intelligence
Threat intelligence gets better too. Analysts used to wade through mountains of data with complicated query languages, manual procedures and reverse engineering just to understand a risk. Now generative AI algorithms can scan code and network traffic for danger on their own, then explain what they found, so analysts can see how a malicious script or other threat actually behaves.
4. Putting Security Patching in Motion Automatically
Patching is tedious. Generative AI can automate both the analysis and the rollout. Using natural language processing (NLP) pattern matching, or a machine learning method called the K-nearest neighbors (KNN) algorithm, it can apply the right fixes or recommend them. Neural networks, meanwhile, comb through codebases looking for vulnerabilities.
5. Enhancing Reaction to Incidents
Incident response is one place generative AI has clearly proven itself. It can draft response plans based on what worked in past incidents, which cuts response times for analysts. As an incident plays out, Gen AI keeps learning and adjusts the plan. And when it’s all over, organizations can have it write the incident response report too.
Examples of Generative AI in Cybersecurity
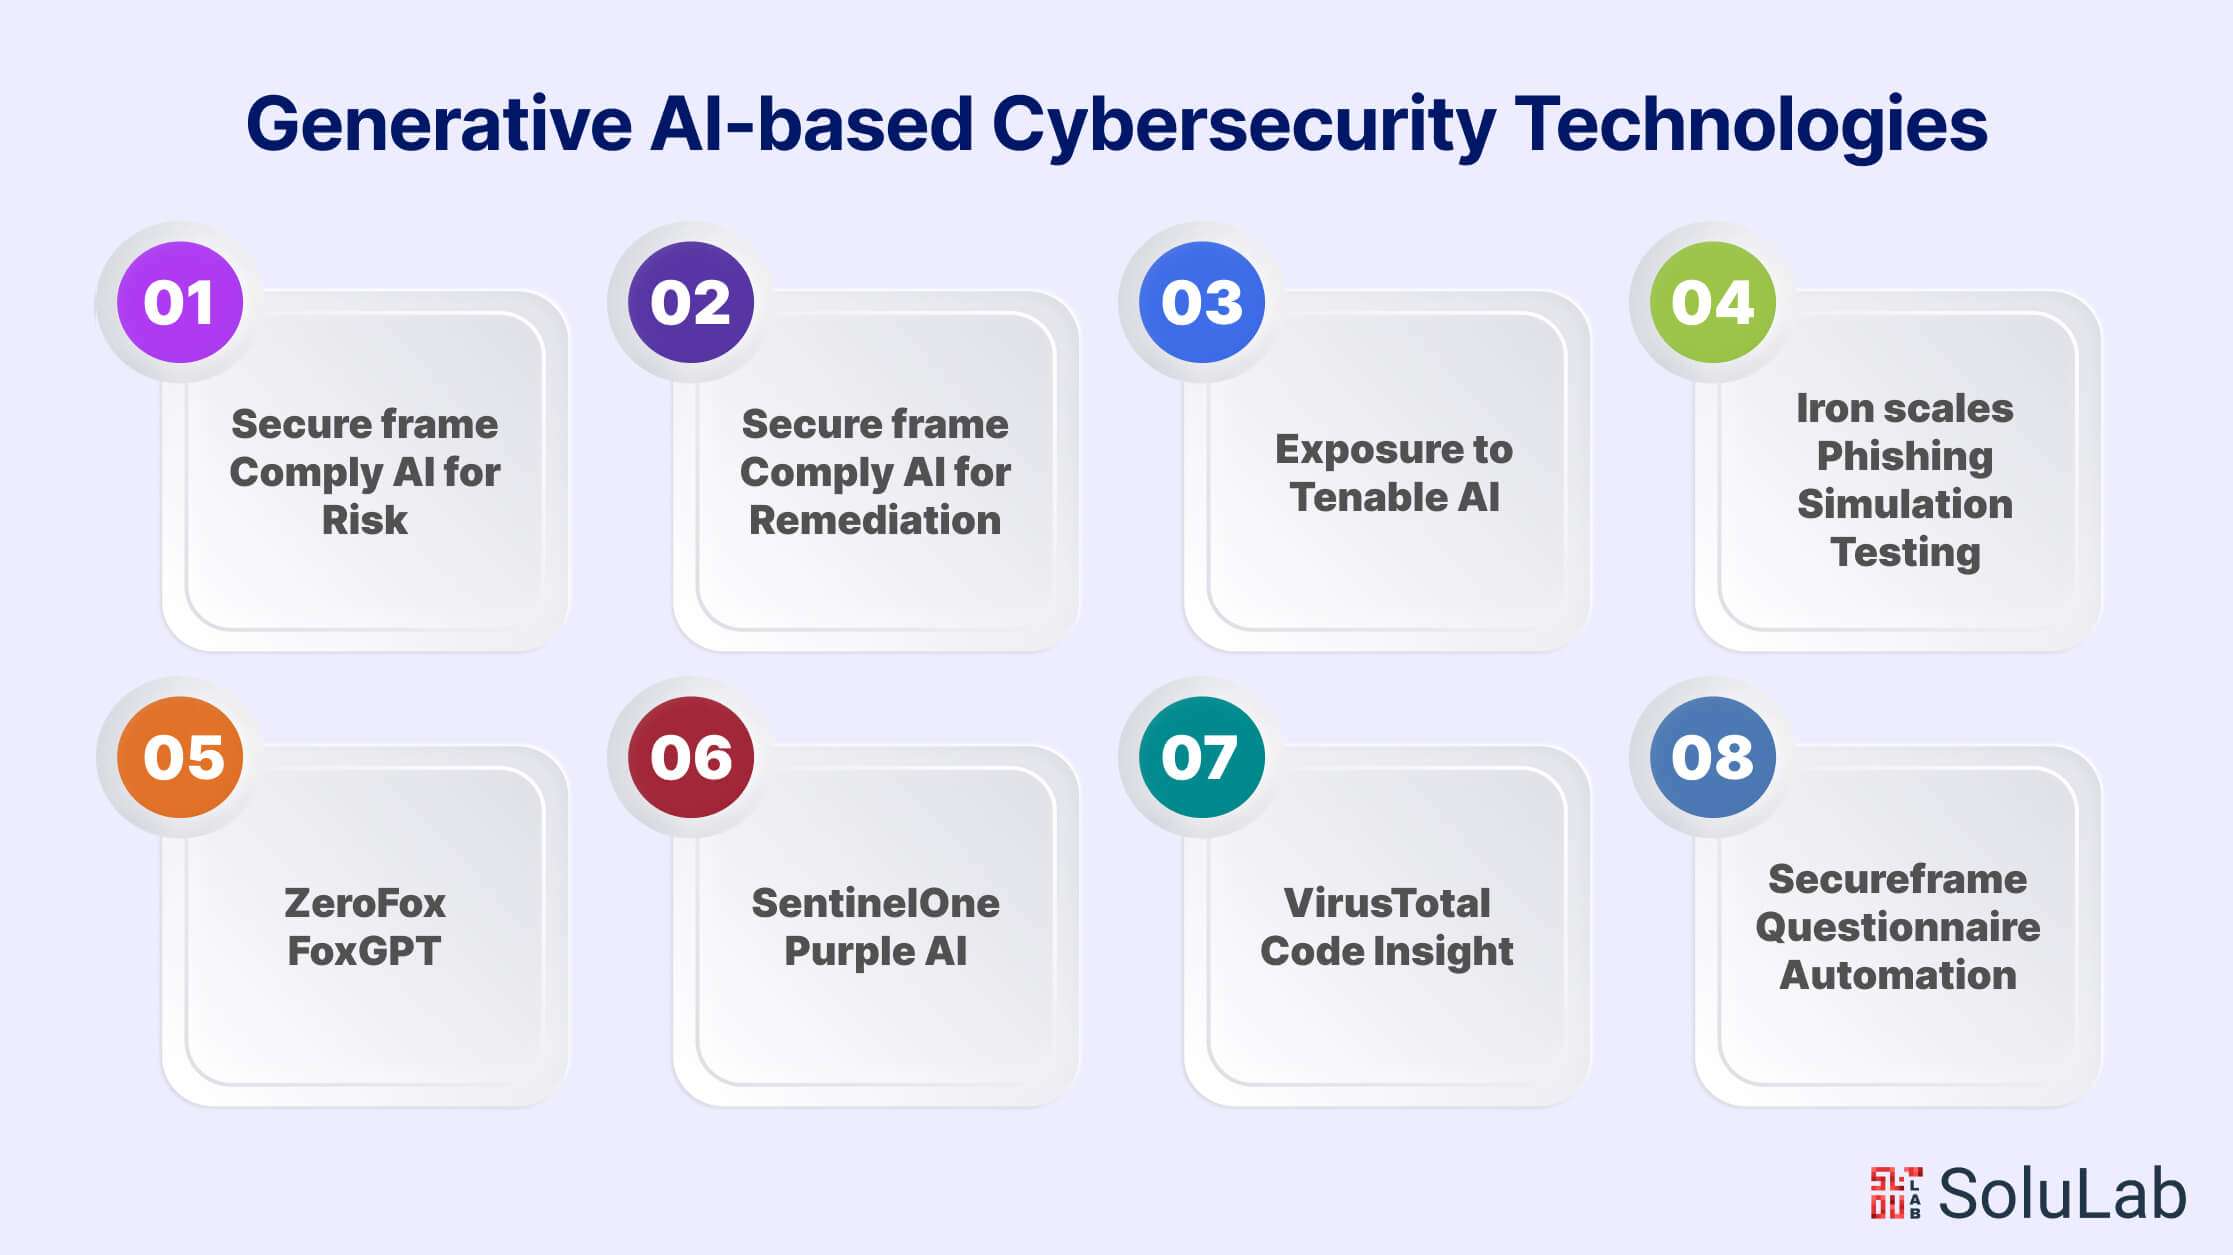
That covers the broad uses. What does this look like in actual products? Here are a few generative AI security tools worth knowing.
Secureframe Comply AI for Risk
Secureframe recently launched Comply AI for Risk to automate risk assessments, which saves businesses both time and money.
Give it a risk description and some company information, and it produces a detailed picture of that risk: how likely it is and how much damage it could do before any response, a treatment plan to deal with it, and the likelihood and impact of whatever risk remains after treatment. With that output in hand, organizations get a clearer sense of what a risk could cost them and which mitigation steps make sense, and they can respond better.
Secureframe Comply AI for Remediation
Secureframe also released Comply AI for Remediation. The aim: give companies a more relevant, accurate and personalized way to fix failed tests and reach compliance faster.
Users get remediation guidance written for their specific environment, so they can fix the root cause behind a failing configuration instead of guessing. The result is that they repair failed controls, pass their tests, tighten their overall security and compliance posture, and get audit-ready quickly.
Stuck on something? There’s a chatbot for follow-up questions, whether you want more detail on the remediation code or advice tailored to your own security and compliance needs.
Exposure to Tenable AI
Tenable built ExposureAI to give analysts new, deeper insight and to make exposure management less of a slog. Its generative AI features help analysts search, analyze and decide on exposures faster by:
- Letting analysts search for specific exposure and asset data by typing questions in plain language.
- Writing up a narrative summary of the full attack path so analysts can see exactly how an exposure could be used.
- Surfacing insights on high-risk exposures and recommending actions, so analysts can decide what to tackle first and deal with it.
Ironscales Phishing Simulation Testing
Ironscales rolled out GPT-powered Phishing Simulation Testing (PST) as a beta feature. It runs on Ironscales’ own proprietary large language model and builds simulated phishing campaigns tailored to individual employees and to the kind of sophisticated phishing attacks they’re likely to face.
The point is speed. Social engineering attacks keep getting more common and more convincing, and this lets companies adapt their security awareness training quickly to keep pace.
ZeroFox FoxGPT
ZeroFox built FoxGPT, a generative AI tool, to analyze and summarize intelligence across large datasets faster. Security teams use it to dig into phishing scams, harmful content and possible account takeovers, and to understand them in context.
SentinelOne Purple AI
SentinelOne announced a threat-hunting platform powered by generative AI. It pairs a large language model (LLM)-based natural language interface with real-time embedding neural networks, so analysts can find, investigate and contain threats faster.
Analysts can ask complex threat and adversary-hunting questions about their environment in plain language and get quick, accurate, detailed answers within seconds. Purple AI doesn’t stop at analyzing threats, either. It can explain observed behavior and suggest what to do next.
VirusTotal Code Insight
VirusTotal Code Insight uses Sec-PaLM, one of the generative AI models available through Google Cloud AI, to describe code snippets in natural language. For a security team looking at a possibly malicious script, that means a quicker read on what the thing actually does. VirusTotal pitches it as a strong helper for security analysts, one that works around the clock and makes them more productive and effective.
Secureframe Questionnaire Automation
Anyone who has filled out a security questionnaire knows the pain. There’s no standard format, no fixed set of questions, no set order, and every customer asks things differently. For security analysts and other stakeholders, it eats hours.
Secureframe’s Questionnaire Automation uses generative AI to take much of that work off your plate. It suggests answers based on previously approved responses plus context and subject matter from the Secureframe platform, which keeps them accurate. Users review the suggestions quickly, tweak whatever needs tweaking, and send the finished questionnaire back to prospects and customers in the same format it arrived in.
The Hazards That Make Cybersecurity For Generative AI Essential
Generative AI promises big leaps in plenty of fields. It also carries security risks you can’t wave away. Most of them come from people misusing AI-generated content: deepfakes, fake news, phishing. And the better these algorithms get, the more urgent strong security becomes, because privacy, security and public trust are all on the line.
These are the main hazards to watch for with generative AI security.
1. Data Overflow: Generative AI services usually let users paste in all sorts of data, private and sensitive material included. That raises a real worry about customer information or intellectual property getting exposed. It’s exactly why generative AI needs proper security controls and safeguards.
2. IP Leak:Web-based Generative AI tools are easy to use. Too easy, sometimes. People start sending and processing data online outside approved systems, and that shadow IT drives up the odds of IP leaks and confidentiality breaches. Techniques such as virtual private networks (VPNs) add another layer of protection by masking IP addresses and encrypting data in transit.
3. Data Training: Training generative AI models takes huge amounts of data. Handle it carelessly and privacy problems follow. You have to make sure confidential information doesn’t slip out by accident, since that could put you on the wrong side of privacy laws.
4. Data Storage: Generative AI models improve as they get more input, which means businesses end up holding more data that has to be stored safely. Put private company information in unsecured third-party storage and it can be misused or leaked. The fix is a thorough data strategy with encryption and access controls built in from the start.
5. Compliance: Generative AI services often send sensitive data off to outside sources. If that data includes personally identifiable information (PII), you’re into compliance territory, and laws like the GDPR or CPRA apply.
6. Synthetic Data: Generative AI can produce synthetic data that looks a lot like the real thing. Close enough, sometimes, to identify specific people or reveal sensitive traits. Handle it with real care so fake data doesn’t end up pointing to real individuals.
7. Unintentional Leaks: A generative model can accidentally repeat bits of its training data that were meant to stay private. So review and validate what these models produce. Their output may contain confidential or sensitive company information.
8. Hostile Attacks and AI Misuse: Bad actors can use generative AI to create deepfakes and misleading content, and that feeds the spread of misinformation and fake news.
Reducing Hazards: An Active Strategy for Generative AI Cybersecurity
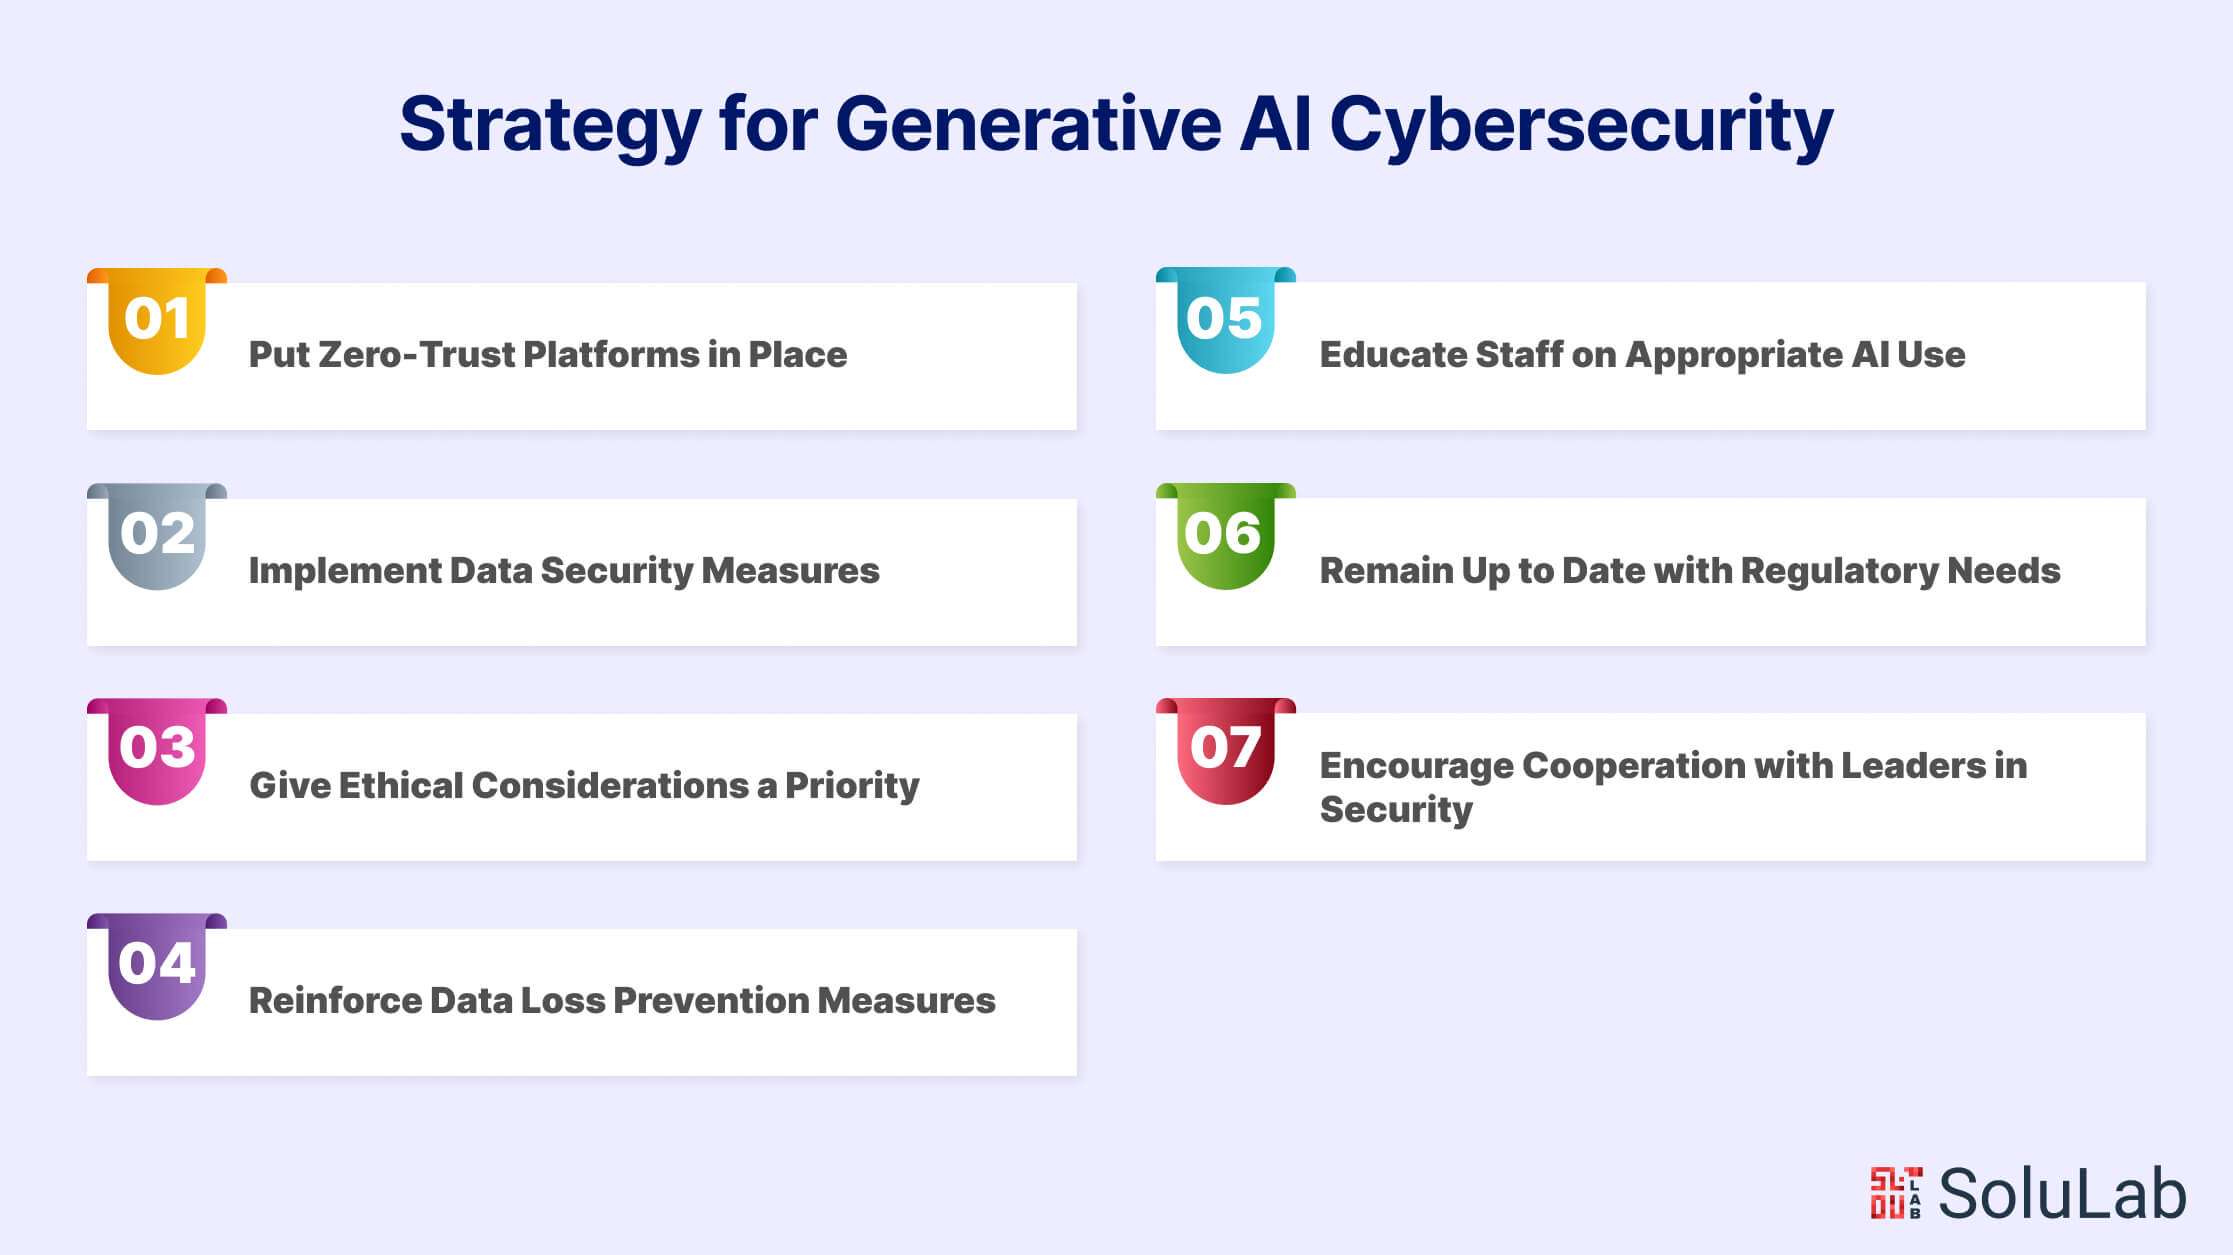
Getting the full value out of generative AI security means acting early and covering every angle, not patching holes one at a time. These are the key ways to cut the risk:
Put Zero-Trust Platforms in Place
Ordinary antivirus software may simply be outmatched by the kind of advanced threats generative AI makes possible. Zero-trust systems built on anomaly detection do a better job of spotting and containing those threats, which lowers the chance of a breach.
Implement Data Security Measures
Build the controls into the model development process itself. Budget for it, too: models have to meet the strictest security requirements, and that costs money. Put data governance frameworks in place to oversee AI projects, tools and teams, so risk stays low and you stay aligned with industry standards.
Give Ethical Considerations a Priority
If your business runs on Generative AI, ethics can’t be an afterthought. Bake ethical checks into day-to-day operations to cut down on bias and keep the technology used responsibly. Skip that, and bias creeps into your data without anyone noticing. What comes out the other end can be an AI product that discriminates.
Reinforce Data Loss Prevention Measures
Protecting digital assets properly means tighter data loss prevention policies at the endpoints and the perimeter. Encryption and access controls, backed by regular audits and risk assessments, go a long way toward keeping out unwanted access and stopping data breaches.
Educate Staff on Appropriate AI Use
People matter here more than any tool. Employees are the ones who keep generative AI use ethical and who make or break its security. Offering Cyber Security Course and training on safe, appropriate AI use helps staff understand the risks and what they could mean for data security and privacy. Give them what they need to question AI output critically and stick to best practices, and risk drops considerably.
Remain Up to Date with Regulatory Needs
Generative AI falls under data protection and privacy laws just like everything else. Companies need to keep track of the latest rules, CPRA, GDPR and industry-specific standards among them. Meet those requirements. Otherwise you’re looking at noncompliance and possible fines.
Encourage Cooperation with Leaders in Security
Work closely with your security leadership. That partnership is how organizations get a real handle on generative AI risks. Spotting risks early, building mitigation plans and enforcing company policy all help protect data privacy and security, and they make your generative AI setup much safer.
Final Words
Generative AI gives almost every industry room to innovate. Just don’t let the excitement crowd out cybersecurity and data privacy. Act early, put strong controls in place, take the ethical questions seriously, and you can get the benefits while keeping the risks small. The practical to-do list is short: stay compliant, train your people, and partner with security professionals. Do those three things and your use of generative AI stays both responsible and secure.
SoluLab, a Generative AI development company, offers modern generative AI services built to back up your cybersecurity work with solutions shaped to your needs. Our AI developers use advanced algorithms to build systems that detect and contain new threats, including deepfakes and AI-generated cyberattacks. With SoluLab, organizations can hire expert AI developersto build custom cybersecurity solutions that protect digital assets and hold up as threats change. Ready to get ahead of the next attack? Partner with SoluLab for your generative AI cybersecurity needs and start securing your digital infrastructure today.
FAQs
Shipra Garg is a tech-focused content strategist and copywriter specializing in Web3, blockchain, and artificial intelligence. She has worked with startups and enterprise teams to craft high-conversion content that bridges deep tech with business impact. Her work translates complex innovations into clear, credible, and engaging narratives that drive growth and build trust in emerging tech markets.