Every organisation keeps adding surface area. More devices, more services, more data moving between them. Attackers noticed years ago, and the campaigns they run now adjust while they are running, which means a defense that only knows yesterday’s attacks ages out fast. Artificial Intelligence (AI) changed what that defense can do, and how quickly it can do it.
This piece traces how AI in cybersecurity actually got here: from blunt rule matching to the deep learning models carrying the load today.
Rule-Based Systems in Cybersecurity
Before AI showed up, security ran on rules. Somebody wrote a signature, the tool matched against it, and whatever matched got stopped. That held up fine against threats already catalogued, and it fell apart on everything else, which is why plenty of companies now lean on managed IT services Dallas providers instead of waiting for the next signature update. Zero-day attacks walked straight through. So did anything that mutated enough to miss the pattern.
Picture antivirus software from that era. It could quarantine a virus only when the file lined up with a signature already sitting in its database. A fresh strain of malware? Invisible, until an analyst wrote a new rule and shipped it. That gap, between a threat landing in the wild and the rules catching up, is where the damage happened.
Machine Learning in Cybersecurity
Machine learning was the first real jump in AI cybersecurity. Rules only ever do what you told them to do. And machine learning systems/algorithms learned from the data itself. They read patterns, picked up on odd behaviour, and caught things nobody had written a rule for. Defense stopped being purely reactive.
Supervised learning let teams train a system on labelled datasets. Feed it enough examples of clean and malicious, and it starts making calls on traffic it has never seen before. A supervised model could pick out known phishing emails, for instance, by recognising the traits they tend to share.
Unsupervised algorithms skipped labels entirely. They studied what normal looked like on a given network, then raised a hand when something drifted from it. Useful against novel attacks. Even more useful against insider activity, where there is no signature to match in the first place.
Semi-supervised learning sat in between: labelled data for threats already understood, unsupervised methods for the rest. Detection accuracy went up. The false positive pile shrank, which any analyst on a rotation will tell you matters more than it sounds.
Reinforcement learning, which most people associate with AI in gaming, turned out to fit here too. It let systems adjust as they went, in real time, rather than waiting on the next training cycle.
Emergence of Deep Learning
Deep learning sits inside machine learning, and it moved the ground under AI cyber-security. Neural networks are the engine here: layered models loosely borrowed from how neurons connect in a brain. Give them enough data and they pull out the features themselves, then reach conclusions a human would need hours to reason through.
Because neural networks handle unstructured input, images, raw text, packet traffic, they turned into serious tools inside cybersecurity systems. Anomaly detection is where they earn their keep, catching the small deviation a threshold rule would never trip. A deep learning model can flag malware it has never encountered, going on how the thing is built and what it tries to do.
Deep learning reshaped phishing defense as well. A network can weigh the wording of a message, how the sender has behaved historically, and the context around the whole exchange, then flag the mail even when none of the familiar phishing tells are there.
Malware detection went the same direction. Models learned to judge code by its structure and its behaviour instead of checking it against a list.
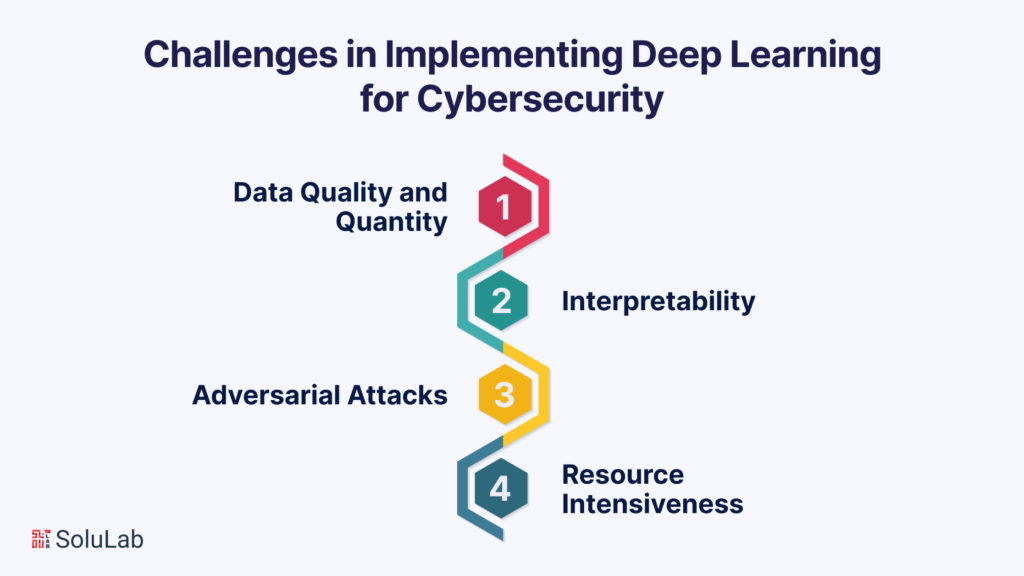
Challenges in Implementing Deep Learning for Cybersecurity
Deep learning opened up a new era of AI development companies, and it dragged a fresh set of problems in behind it.
- Data Quality and Quantity: These models are hungry. Assembling large, clean, labelled training sets for AI cybersecurity services is hard work, and the data goes stale while you are still collecting it, because the threats keep moving.
- Interpretability: Deep neural networks are famously “black boxes.” Ask one why it called a process malicious and you often get nothing usable back. That hurts during incident response. It hurts more during forensics, when somebody has to defend the decision to a room full of people.
- Adversarial Attacks: Attackers study the defenses. Adversarial inputs nudge data just enough to fool the model while looking perfectly ordinary to everyone else, and this is a practical problem rather than a theoretical one.
- Resource Intensiveness: Training and running these models costs compute, and plenty of it. For a smaller organisation with modest IT infrastructure, that alone can end the conversation.
Ethical Concerns Surrounding AI in Cybersecurity
- Privacy: Deep learning systems chew through personal data by design. The boundary between monitoring a network and watching the people on it gets thin quickly, and holding that line is most of the job.
- Bias and Fairness: Models inherit whatever bias lives in their training data. If that data skews by race, gender, or any other attribute, the security system carries the skew forward and treats some groups differently without anyone intending it.
- Transparency: Back to the black box problem. When you cannot explain a decision, accountability suffers, and so does compliance with any regulation that demands an explanation for what the system did.
- Over-Reliance on AI: AI makes a security team better. It also makes them comfortable. Pull humans out of the loop and complacency creeps in, so the professionals need to stay on the decisions that matter and supply the context the machine is missing.
Real-World Examples
None of that has slowed adoption. A long list of organisations run deep learning for cybersecurity today, with results worth pointing at:
- Darktrace: Darktrace runs unsupervised machine learning and AI to spot threats and answer them as they happen. Its “Enterprise Immune System” learns how one specific network normally behaves, then treats departures from that baseline as a signal worth acting on.
- Cylance: Now part of BlackBerry, Cylance uses AI-driven detection to stop malware and other threats before they execute. The approach rests on Generative AI tools trained against both known and unknown threats.
- FireEye: FireEye’s Mandiant Threat Intelligence applies AI and machine learning for cybersecurity to find threats and respond to them, using deep learning for fast detection and bolting automated response onto the back of it.
- Google’s Chronicle: Chronicle, a Google subsidiary, gives organisations a platform that runs machine learning over their network data to analyse it and surface threats.
These are shipping products, not lab demonstrations. Organisations are buying and running them because the window for responding to an attack keeps getting shorter.
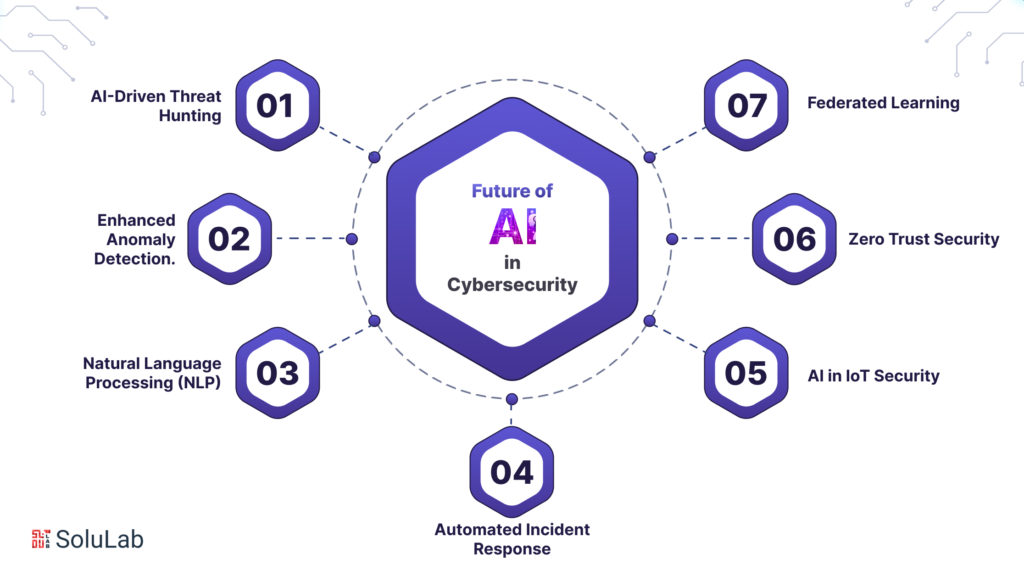
The Future of AI in Cybersecurity
So where does this go next? A handful of threads are worth watching:
- AI-Driven Threat Hunting: Threat-hunting tooling keeps getting sharper. Standing it up properly usually calls for solid managed security operations center (SOC) services that pair automated monitoring with people who know what they are looking at.
- Enhanced Anomaly Detection: Deep learning models keep improving at noticing small, quiet deviations from normal behaviour, which is exactly what you need against a patient attacker who is trying not to be seen.
- Natural Language Processing (NLP): NLP is being pointed at text-based attacks: phishing mail, social engineering attempts, the messages written to sound like a colleague. Catch those early and most of the chain never starts.
- Automated Incident Response: AI now handles parts of the response, not just the detection. Systems can act on a threat in real time and take some weight off a team that is already stretched.
- AI in IoT Security: There are more connected devices every quarter, and a lot of them were never designed with security in mind. Machine learning models are being used to watch for unusual behaviour or weak points across those device fleets and the networks holding them together.
- Zero Trust Security: Zero trust runs on constant verification, and AI does much of that checking. Who is this user, is the device still in good shape, should this particular request go through at all.
- Federated Learning: This one lets organisations work on threat detection together without handing over sensitive data. Generative AI models are trained collectively, so shared intelligence gets stronger while everyone keeps their own logs to themselves.
The Evolving Role of Human Experts
AI is a strong ally against cyber threats. It is not a substitute for people, and the reasons are specific:
- Contextual Understanding: People bring context. They know the quirks of their own environment, the system that always looks strange, the team whose workflow trips every rule written. That local knowledge is difficult to model and easy to underrate.
- Adaptation and Innovation: Adversaries change tactics constantly. Human defenders change with them, inventing responses that no model was trained on, which is how you stay a step ahead instead of a step behind.
- Ethical Decision-Making: Judgement calls about privacy, compliance, and how far to push AI itself land on people. There is no model for values.
- Complex Investigations: A serious incident needs investigators. Someone has to assemble the fragments, connect the technical evidence to the wider picture of who is attacking and why, and decide what it all means.
So the future here is a collaboration between human expertise and artificial intelligence. AI absorbs the volume and the pattern work, and the people get their attention back for the parts that genuinely require thinking.
Conclusion
The road from AI built on rules to AI built on deep learning covered a lot of ground, and what defenders hold in their hands now is far better than what came before. It is also unfinished. Data privacy and model bias remain open problems, and the human experts running these systems still make the calls that decide whether a bad day becomes a breach.
The teams that hold up under pressure treat AI as an amplifier for their analysts rather than a replacement for them. Human judgement plus machine speed. That pairing is the defense, not either half on its own.
SoluLab works in exactly this territory. AI development services and hire AI developers sit at the centre of what the team builds, and cybersecurity is one of the places that work lands. The approach is the one described above: deep learning applied to defenses that move before an attacker does, instead of after. For organisations that would rather build the capability internally, SoluLab also offers AI development services and AI developer hiring.
FAQs
Shipra Garg is a tech-focused content strategist and copywriter specializing in Web3, blockchain, and artificial intelligence. She has worked with startups and enterprise teams to craft high-conversion content that bridges deep tech with business impact. Her work translates complex innovations into clear, credible, and engaging narratives that drive growth and build trust in emerging tech markets.