Introduction
A smart contract audit is a structured security review of contract code, logic, and economic design carried out before deployment, combining manual expert review, automated analysis, and, in high-value cases, formal verification. It exists because on-chain code is public, adversarial, and in most cases permanent. Fixing a flaw after launch is rarely an option.
The numbers make the case better than any argument. The DAO hack took $60 million. The Poly Network exploit cost $611 million. The Ronin Bridge breach drained $625 million. Across 2024 as a whole, Immunefi recorded $1.49 billion lost across 232 incidents, with hacks accounting for 98.1 percent of that total and DeFi protocols absorbing 51.4 percent of the losses.
This guide covers how smart contracts work, what an audit actually involves step by step, how manual review, automated tooling, and formal verification divide the work between them, what an audit costs, how to tell whether your code is ready to be audited, what an audit cannot promise you, and what happens after deployment. Whether you are a founder preparing to launch, a developer building on a new protocol, or a business evaluating smart contract auditing companies, everything you need to make the call is here.
Key Takeaways
- The problem: Most smart contract failures do not come from exotic exploits. They come from basic oversights made before deployment: unchecked assumptions, excessive scope, weak access control, and underestimating how long a real audit takes. Once the contract is live, those mistakes get expensive or become permanent.
- The solution: A structured audit checklist forces you to review risk, scope, dependencies, upgrade paths, and failure scenarios while changes are still cheap and architecture can still be corrected.
- How SoluLab can help: SoluLab applies this checklist in real builds through pre-audit consulting, security-first architecture, and audit-ready smart contract development that reduces deployment risk, shortens audit cycles, and cuts long-term technical debt.
How Smart Contracts Work Before Deployment and Audit?
A smart contract is an agreement written in code that executes automatically when its conditions are met, deployed to a blockchain where no bank, lawyer, or intermediary is needed to enforce it. Once deployed, the rules are fixed, and the contract runs without approval from anyone.
That removal of human dependency is the real shift. It cuts time and cost out of execution, and it also removes the safety net. There is no one to call when the logic is wrong.
By 2026, these are not simple if-then scripts. They are modular systems using account abstraction, cross-chain messaging, and zero-knowledge proofs. They run on EVM chains like BNB Chain, Polygon, and Avalanche, on non-EVM ecosystems such as Solana, Cardano, and Aptos, and across Layer 2s including Optimism, Arbitrum, and zkSync. Most production deployments now involve Ethereum blockchain development alongside at least one Layer 2 target.
In practice, that means contracts are more flexible, more portable, and far closer to production-grade software than early versions ever were. It also means the attack surface is larger than a single codebase.
Where Are Smart Contracts Used in 2026?
Smart contracts now underpin lending and trading protocols, supply chain verification, tokenized real estate, DAO governance, parametric insurance, and milestone-based B2B payments. Anywhere value moves between parties who do not fully trust each other, contract code is doing work a settlement team used to do manually.
- Financial Services: Automated market makers, flash loan systems, lending protocols, insurance payouts, and tokenized asset management all run on contract logic. DeFi development is where the largest value concentrations sit, which is also why it attracts the most sophisticated attackers.
- Supply Chain Management: Contracts automate verification, payment release, and audit trails, with every transaction timestamped and traceable. When a dispute happens, the record already exists.
- Real Estate and Tokenized Assets: Property platforms use contracts to manage fractional ownership and distribute rental income automatically in stablecoins, without manual reconciliation. Asset tokenization platforms handle registry, compliance, and transfer logic in the same contract layer.
- Token Offerings and DAOs: Token sales, treasury management, and governance voting execute transparently through code, with proposals and outcomes recorded on-chain.
- Insurance With Parametric Payouts: Payouts trigger automatically on oracle-verified real-world events such as flight delay length or rainfall thresholds, removing the manual claims process entirely.
- Milestone-Based B2B Payments: Funds release after delivery confirmation, with automated revenue sharing across multiple parties in a single transaction.
- Multi-Chain Applications: Contracts deployed across several chains need compatibility verification at every target, because behaviour that is safe on one chain is not automatically safe on another.
What Smart Contract Security Risks Do Most Teams Miss Before Deployment?
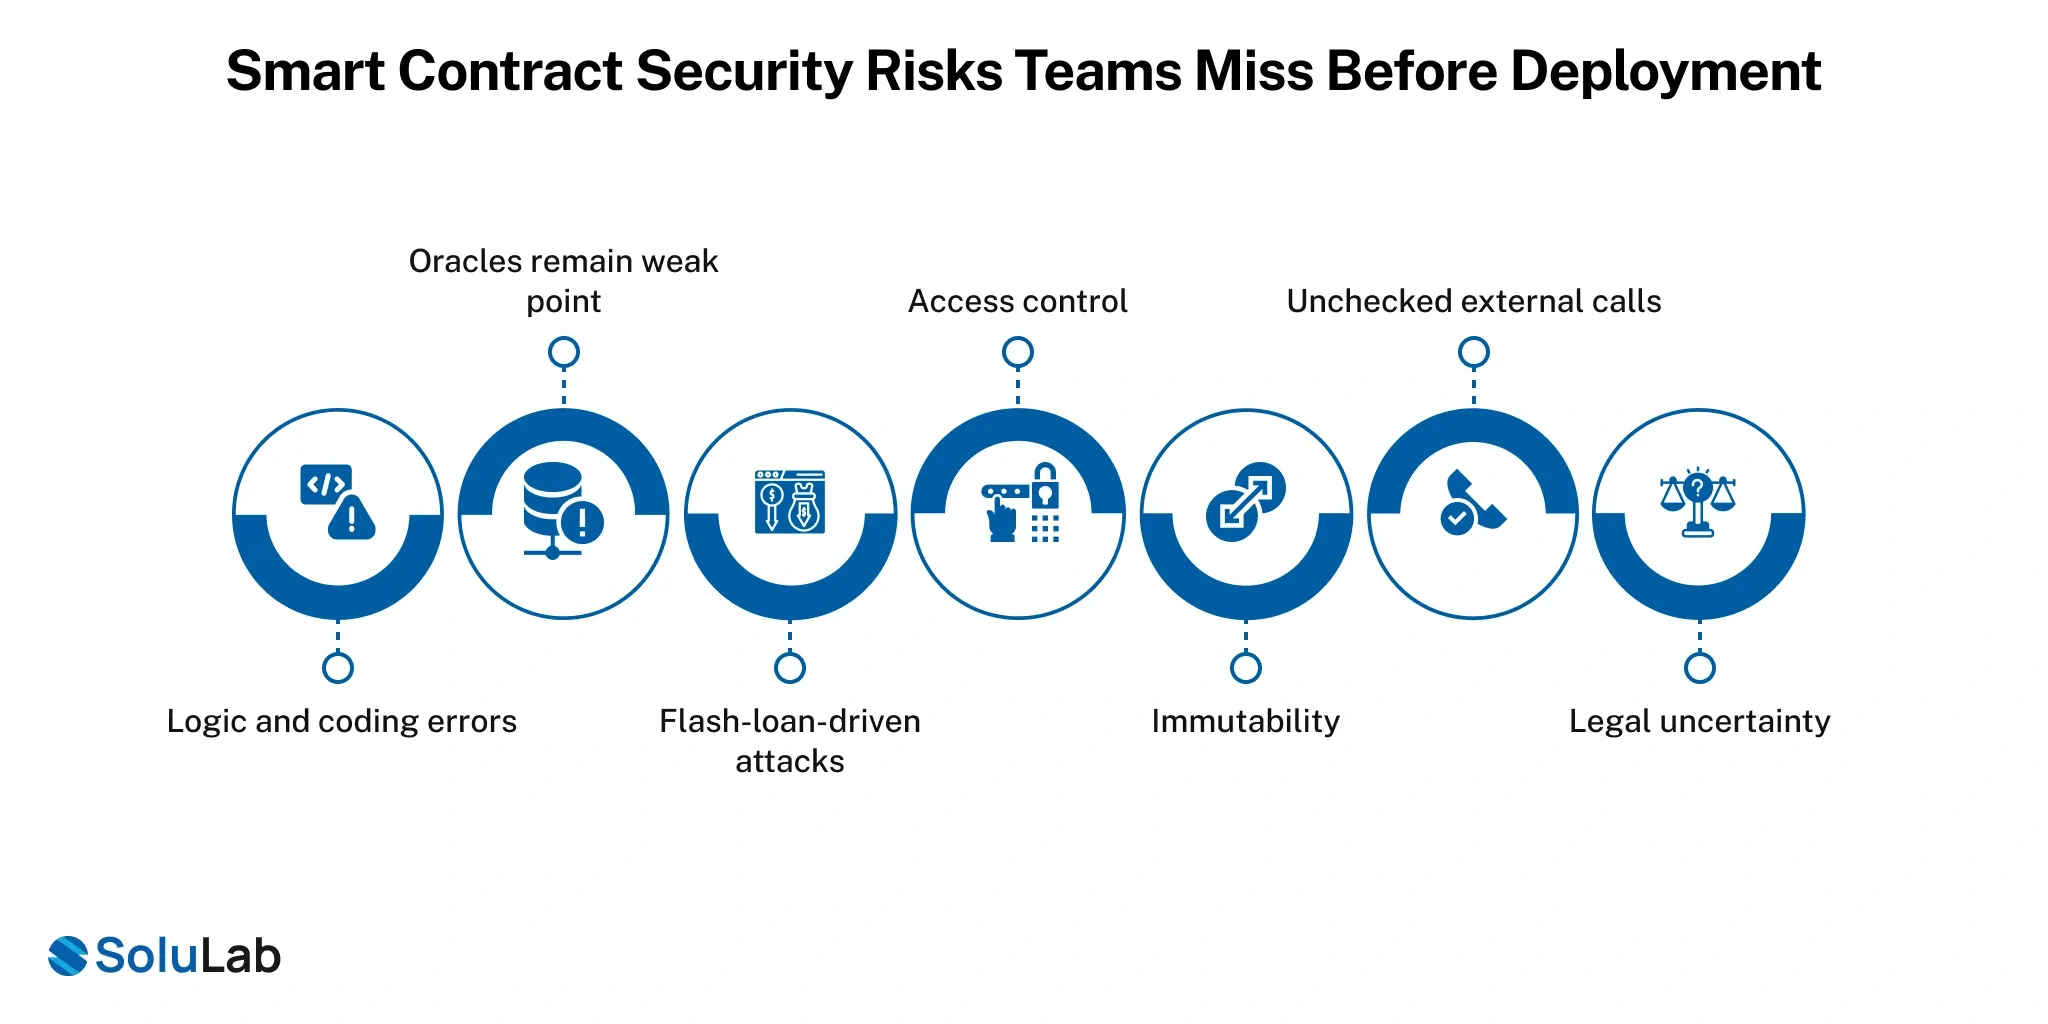
The risks that cause real losses are rarely exotic. According to the OWASP Smart Contract Top 10 for 2026, access control vulnerabilities rank first, followed by business logic flaws, price oracle manipulation, and flash loan-facilitated attacks. Most teams underestimate all four:
- Access Control Failures: Ranked SC01:2026 by OWASP and backed by 2025 incident data showing roughly $220 million lost across 30 separate incidents in this category alone. Misconfigured permissions stay at the top of the list because once the wrong address has privileged access, every other control becomes irrelevant.
- Business Logic Flaws: SC02:2026 and the category with the largest single incidents in OWASP’s 2025 dataset. These are cases where the code does exactly what the developer intended, but the intention itself creates the vulnerability. Broken reward formulas, incorrect minting logic, and flawed collateral calculations all sit here.
- Price Oracle Manipulation SC03:2026: If your contract depends on external data, that dependency is an attack surface. Single-source price feeds and thin liquidity pools remain the most exploited weak point in DeFi.
- Flash Loan Facilitated Attacks SC04:2026: These use large uncollateralized loans inside a single transaction to manipulate on-chain state before the system can react. They are not a vulnerability in themselves; they are an amplifier that turns a small logic gap into a total drain.
- Unchecked External Calls SC06:2026: Silent failures from unchecked return values cause enough damage that current Solidity development standards require explicit return checks, try-catch handling, and strict validation on every external interaction.
- Proxy and Upgradeability Flaws: SC10:2026, and new to the list this cycle. Upgradeable contracts introduce storage collision risks, uninitialized implementation contracts, and admin key exposure. Teams add upgradeability to reduce risk and frequently increase it instead.
- Immutability and Legal Uncertainty: Once a contract is live, changing it is hard or impossible. Many teams now run hybrid autonomy, letting contracts operate automatically day to day while allowing human intervention during emergencies.
Separately, enforcement and legal recognition still vary by jurisdiction, so contracts do not live in a legal vacuum no matter how autonomous they look.
What Are the Benefits of a Smart Contract Audit Before Deployment?
An audit protects capital, surfaces design flaws that testing misses, unlocks exchange listings and institutional partnerships, and gives users a verifiable trust signal. For any contract holding meaningful value, the audit fee is small relative to the exposure it covers.
- It Protects Financial Exposure. The cost of a single exploit typically exceeds the cost of an audit by orders of magnitude. For a protocol holding significant user funds, the fee is not an expense; it is insurance with a measurable premium.
- It Builds Trust Before You Need It. Users and investors evaluating a new protocol look for audit reports the same way they look for financial statements in traditional markets. A clean report from a credible firm reduces friction at the point of acquisition.
- It Surfaces Design Flaws, Not Just Code Bugs. The best audits catch cases where the code is correct, but the design is exploitable. These issues are more dangerous than surface-level bugs precisely because they survive a passing test suite.
- It Satisfies Listing and Partnership Requirements. Many exchanges, aggregators, and institutional partners require an audit report before they will list or integrate a protocol. Skipping it does not just raise risk; it can close your route to market.
- It Is Mandatory for Enterprise Deployment: Any organization deploying contracts at scale through blockchain development services will be required by legal and compliance teams to show that the code has been professionally reviewed.
Why Does a Smart Contract Audit Actually Matter Before Deployment?
Because deployment is usually irreversible and the code is public from the moment it lands. Anyone can read it, fork it, simulate against it, and probe it continuously. An audit is the last point at which a design decision is still cheap to change.
- Security Is Not Abstract Here. Your contract is readable by every attacker on the network the second it deploys. Access control issues and unchecked calls do not announce themselves, they drain quietly. Modern audits matter because they simulate how the contract breaks rather than only reading whether it compiles.
- The Money Does Not Come Back: When a contract fails, the loss is usually permanent. Oracle manipulation and flash loan attacks remain the fastest routes to pulling value out of a protocol, and neither has a rollback.
- Compliance Is Part of the Job Now. Audits are no longer purely technical. Under frameworks like MiCA in Europe and emerging rules in the US and Asia, audit documentation has become part of the compliance record. A good audit reduces legal exposure and demonstrates that you intend to operate long term.
How Are Smart Contract Audits Performed, Step by Step?
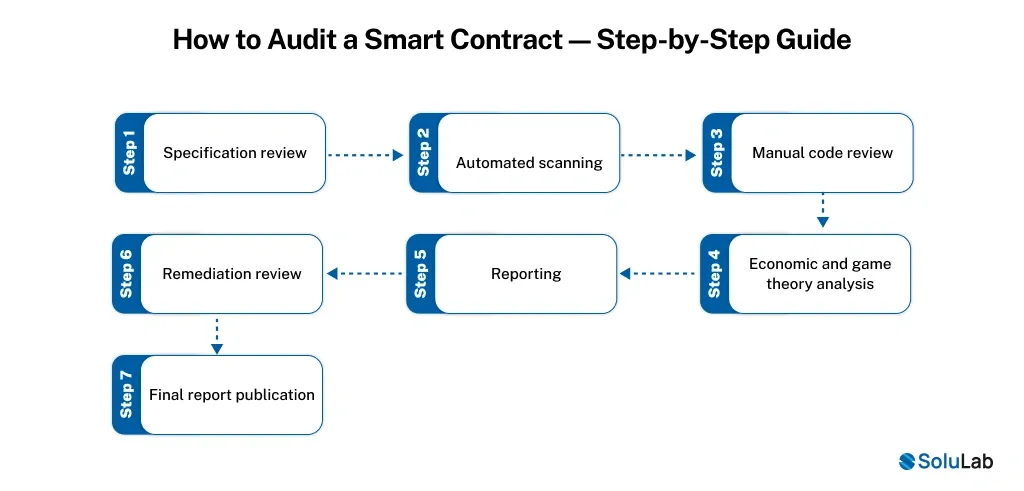
A credible audit runs seven stages: specification review, automated scanning, manual code review, economic analysis, severity-ranked reporting, remediation review, and final report publication. Any engagement missing the remediation stage is an incomplete audit, not a cheap one.
- Specification Review: Before touching code, the auditor reads the documentation, the whitepaper, and any available specification of intended behaviour. Auditing code without understanding intent produces a checklist review, not a security audit.
- Automated Scanning: Tools run first to flag known vulnerability patterns quickly. Static analysis catches reentrancy patterns, arithmetic issues, unchecked return values, and access control gaps across the whole codebase in minutes. This stage clears the surface efficiently so human time goes somewhere harder.
- Manual Code Review: Experienced auditors read the code line by line. Here, the smart contract functions are evaluated not only for correctness but for economic security, meaning whether a sophisticated actor can exploit the logic even when it behaves exactly as designed. Most serious findings come from this stage.
- Economic and Game Theory Analysis: For DeFi protocols, this stage tests whether incentive mechanisms can be gamed. Flash loan sequencing, oracle manipulation, sandwich attacks, and liquidity pool exploits are economic vulnerabilities that require protocol-specific expertise rather than general code review.
- Severity-Ranked Reporting: The auditor produces a report categorizing findings as critical, high, medium, low, or informational. Each finding includes the vulnerability, its potential impact, and a recommended remediation. A report without severity ranking is not usable for prioritization.
- Remediation Review: After your team fixes the findings, the auditor verifies the fixes resolved the issue without introducing new ones. This stage is non-negotiable. Skipping it is how projects ship a “passed” audit with live bugs in the patched code.
- Final Report Publication: A clean final report is published, typically on both the auditor’s site and the project’s documentation, serving as the verifiable public record. If you are comparing a smart contract audit company against others, read their published reports before you read their marketing.
What Are the Three Layers of a Real Smart Contract Audit?
A real audit is three independent checks, not one. Manual expert review catches intent and design flaws. Automated analysis catches pattern-based bugs across the full codebase. Formal verification mathematically proves specific properties always hold. Each layer catches a class of bug the other two structurally cannot.
Most of what gets sold as an audit is a tool dump with a report template around it. The difference is whether the layers are genuinely independent.
- Manual Expert Review catches what requires understanding. Design-level flaws, incorrect assumptions about how users behave, and economic attacks that need protocol context. A human is the only layer that can judge whether the intended behaviour is itself a problem. It is also the slowest and most expensive layer, and its coverage depends entirely on the reviewer’s experience with your protocol type.
- Automated Analysis: Static and Fuzzing Catch what requires exhaustiveness. Static analysis tools such as Slither and Aderyn scan every path in the codebase for known dangerous patterns. Fuzzers such as Echidna, Medusa, and Foundry’s invariant testing throw millions of randomized input sequences at the contract to find states a human would never think to try. Machines do not get bored at line 4,000. Humans do.
- Formal Verification catches what requires proof. Rather than testing many cases, it mathematically demonstrates that a stated property holds for every possible input. The next section covers when that is worth paying for.
The argument for layering is simple. A fuzzer will find an arithmetic edge case a reviewer skimmed past. A reviewer will find an access control design flaw that every tool reports as clean because the code is technically correct. Formal verification will prove an invariant holds where both of the others could only sample.
Running one layer and calling it an audit leaves the other two classes of bugs in your contract. Quality smart contract audit services will tell you which layers they ran and why.
What Is Formal Verification, and When Is It Worth the Cost?
Formal verification uses mathematical proof to demonstrate that a contract satisfies a stated property under every possible input, rather than testing a finite number of cases. Where an audit finds bugs, formal verification proves the absence of a specific class of bug. It is the strongest guarantee available and also the most expensive.
How It Differs From an Audit?
An audit asks: can an expert find something wrong with this? Formal verification asks: can this property ever be violated? The distinction matters. An audit can miss a bug because nobody thought to look for it. A proof cannot miss a violation of the property it proves, because it covers the entire input space rather than sampling it.
The limitation is equally sharp. Formal verification only proves what you specify. If your specification is wrong, or if it omits the property that actually gets exploited, the proof is correct and useless. Writing good specifications is the hard part, and it takes protocol expertise rather than tooling.
What It Actually Involves
You define invariants in a specification language. Total supply always equals the sum of balances. A user can never withdraw more than they deposited. An admin function can never be called by a non-admin. A prover such as Certora, Halmos, or Kontrol then attempts to find any execution path that violates the stated invariant. If it finds one, you get a counterexample. If it does not, you get a proof.
When It Is Worth the Cost
Formal verification typically makes sense in four situations:
- The contract holds or will hold very large value, where the cost of the proof is small relative to the exposure.
- The logic is mathematically dense, such as AMM pricing curves, interest accrual, or liquidation thresholds, where edge cases are hard to reason about informally.
- The contract is immutable with no upgrade path, so there is no way to patch a discovered flaw later.
- An institutional counterparty, insurer, or regulator requires a demonstrable correctness guarantee rather than a best-effort review.
When It Is Overkill
For a standard token contract using a well-audited library implementation, formal verification adds cost without adding much certainty, because the library has already been verified and the surface is small. For an early-stage protocol still changing its design weekly, verification is premature. You would be proving properties about code that will not exist next month. Spend that budget on a proper manual audit first, then verify once the design is stable.
Most projects should treat this as a second-phase investment rather than a launch requirement.
What Are the Core Components of a Smart Contract Audit Checklist?
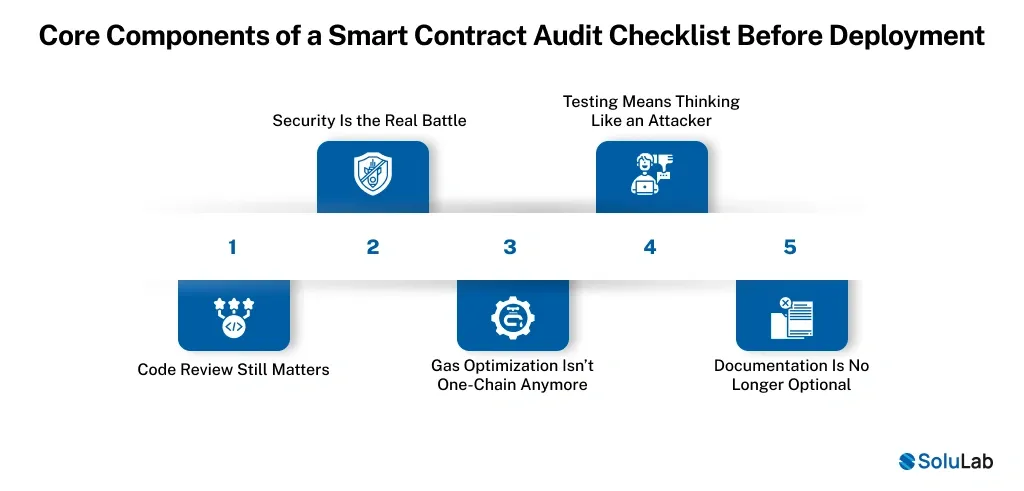
A complete checklist covers five areas: code quality, security, gas behaviour across every target chain, adversarial testing, and documentation. In 2026, the emphasis has shifted from reading code to predicting behaviour once the contract is live, connected, and holding real value.
- Code Quality and Structure: Still the foundation. Automated tooling now catches obvious logic and structural issues early, which frees human reviewers to focus on what actually breaks contracts: bad assumptions, edge cases, and flows that look correct on paper and fail under load.
- Security and Attack Surface: Access control failures remain the top-ranked risk, while flash loan sequencing and oracle manipulation continue to drain capital. Multi-chain setups, particularly bridges and cross-chain messaging, raise the stakes sharply because a flaw on one chain becomes a flaw everywhere the contract is deployed.
- Gas Behaviour Across Every Target Chain: Gas strategy is no longer a single-chain question. What is efficient on Ethereum mainnet is not automatically efficient on Arbitrum, Optimism, or zkSync, and calldata pricing differs enough between Layer 2s to change which implementation is correct. Audits should check performance on every chain you intend to deploy to, not just the one you developed on.
- Adversarial Testing: Testing now means thinking like an attacker. Flash loan simulations, reentrancy loops, oracle price swings, and forked mainnet scenarios are standard because they reflect how real exploits happen. If those scenarios are not tested, the audit is incomplete. This matters most for DEX smart contract development, where liquidity math and price impact create an attack surface that unit tests will not reach.
- Documentation and Traceability: Documentation used to be an afterthought. It is now tied to accountability. Clear on-chain annotations, version control, and audit trails are expected, particularly as compliance requirements and post-incident reviews become routine.
At this point, an audit is less a checklist and more a system review. Teams that treat it seriously do not just look for bugs; they look for failure modes.
What Does a Smart Contract Audit Cost in 2026?
Smart contract audit costs range from roughly $2,000 for a standard token contract to $50,000 and above for enterprise multi-chain systems. Price is driven by four variables: contract complexity, lines of code, target blockchain, and the reputation and methodology of the auditing firm.
| Audit Type | Typical Scope | Estimated Cost |
| Basic token contract | ERC-20 or ERC-721, standard functions | $2,000 to $5,000 |
| Mid-complexity protocol | DeFi, staking, governance contracts | $7,000 to $20,000 |
| Full DeFi protocol | Multi-contract system, complex economics | $30,000 to $60,000 |
| Enterprise or institutional | Custom architecture, multi-chain, compliance layer | $50,000 and above |
| Formal verification add-on | Invariant specification and proof, per property set | Typically 1.5x to 3x the base audit |
The lowest band covers straightforward token contracts with standard functions and limited external interactions. Appropriate for a simple launch, insufficient for anything holding meaningful user funds.
The mid band covers most DeFi protocols: staking systems, liquidity pools, governance mechanisms, and multi-contract interactions. This is where the majority of projects should budget.
The upper bands cover full protocol deployments, cross-chain bridge logic, and custom tokenomics with real game theory exposure. A structured blockchain consulting engagement before the audit usually reduces the final quote, because scope gets defined before the auditor has to discover it.
One honest point. Audit cost should be evaluated against value at risk, not against your development budget. A protocol holding $10 million that skips a $20,000 audit to save money is not being capital-efficient. A single exploit at that scale costs several hundred times the audit fee.
How Do You Know If You Are Ready for a Smart Contract Audit?
 Smart Contract Audit Readiness Before You Call an Auditor” class=”wp-image-185170″/>
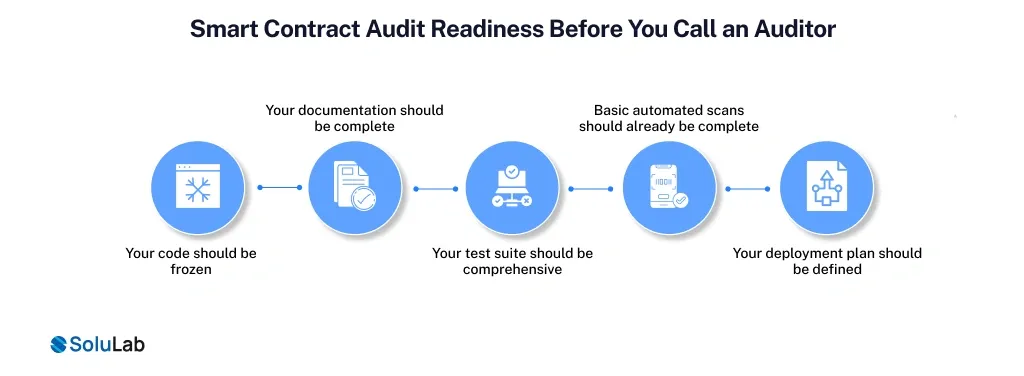
You are ready when your code is frozen, your documentation is complete, your test coverage is above 90 percent, you have already run automated scans yourself, and your deployment plan is defined. Most founders contact an auditor well before this point, which wastes calendar time and inflates the quote.
- Your Code Should Be Frozen. An auditor cannot audit a moving target. The version you submit should be the version you intend to deploy. Changes made after the audit begins trigger scope reassessment and usually a new quote.
- Your Documentation Should Be Complete. The auditor needs to know what the contract is supposed to do before judging whether it does so securely. Provide a specification, a description of each function, and any known edge cases or deliberate design trade-offs. Write down the invariants you believe should always hold, even informally. That list is the single most useful document you can hand an auditor.
- Your Test Suite Should Be Comprehensive. A well-tested codebase is faster and cheaper to audit because expected behaviour can be verified through existing tests rather than reconstructed from the code. Aim for above 90 percent coverage before submitting, and include invariant tests rather than only unit tests.
- Basic Automated Scans Should Already Be Done. Run Slither and a Foundry fuzzing pass yourself before engaging anyone. This removes the easy findings from the report and directs paid time toward the complex, high-severity issues that tooling misses. Note that MythX, long a default in this step, was shut down by Consensys on 31 March 2026, so any guide still recommending it is out of date.
- Your Deployment Plan Should Be Defined. The auditor needs to know how the contract will be deployed, in what order, with what initial parameters, and who holds administrative access afterward. Deployment is itself a security-critical process and belongs inside the audit scope. Working with a smart contract development company that builds toward audit readiness from the start typically removes an entire review cycle.
Who Should Not Get a Smart Contract Audit Yet?
Some teams should delay. If your protocol design is still changing weekly, if you have not written tests, if your contract holds no value and has no users yet, or if you cannot articulate what your contract is supposed to guarantee, an audit now is money spent on a snapshot you are about to invalidate.
Three situations where waiting is the better call:
- The design is not settled. Auditing a protocol whose economic model changes next sprint means paying for findings against code that will not ship. Stabilize the architecture first.
- There are no tests. If the auditor has to reconstruct intended behaviour from the code, you are paying senior security rates for work your own team should do. Build the test suite, then audit.
- The contract is a prototype with no value at stake. A testnet demo with no user funds does not need a $20,000 review. It needs a security-aware developer and a Slither run. Audit before mainnet, not before the pitch deck.
Being told to wait is not a rejection. A firm that takes your money to audit code that is not ready is not doing you a favour.
What Smart Contract Audit Tools Are Used in 2026?
The current toolchain splits across static analysis, fuzzing and property testing, symbolic execution, formal verification, and live monitoring. Serious teams use tools from every category rather than choosing between automation and human review.
| Category | Current Tools | What It Catches |
| Static analysis | Slither, Aderyn, Solhint | Known dangerous patterns across every path in the codebase |
| Fuzzing and property testing | Echidna, Medusa, Foundry invariant tests | Edge-case states reached through randomized input sequences |
| Symbolic execution | Mythril, Halmos | Reachability of specific problematic states across input ranges |
| Formal verification | Certora Prover, Kontrol, Halmos | Mathematical proof that a stated invariant always holds |
| Live monitoring | OpenZeppelin Defender, Forta, Tenderly Alerts | Anomalous gas patterns, unusual access, oracle deviation post-launch |
| CI integration | GitHub Actions, Foundry CI | Regression checks on every commit and pull request |
Two things worth knowing about this table. First, MythX and Securify appear in most competing guides and neither should be in your 2026 pipeline. Consensys shut MythX down in March 2026, and Securify has not been actively maintained for years. Second, Echidna and Mythril are frequently miscategorized as manual inspection tools. They are not. Echidna is a fuzzer and Mythril is a symbolic execution engine. Both are automation.
The larger shift is what happens after deployment. Monitoring platforms now watch live contracts continuously for irregular gas usage, unusual access patterns, and signs of oracle manipulation, so teams get alerts while containment is still possible rather than discovering the problem in a post-mortem. Any team shipping dApp development work to mainnet should have monitoring configured before launch day, not after.
Can a Smart Contract Audit Guarantee 100 Percent Security?
No. An audit substantially reduces risk, it does not eliminate it. Audited protocols are exploited regularly, because an audit is a time-boxed review of a specific code version by a finite number of people, and because entire categories of risk sit outside the code the auditor reads.
Being direct about this matters more than it costs. Here is what an audit does not cover:
- Code that changed after the review. The audit covers the exact commit submitted. Post-audit modifications, however small, are unaudited code.
- Risk introduced by dependencies. Your contract may be sound while the oracle, bridge, or external protocol it calls is not. Composability means inheriting someone else’s attack surface.
- Key and governance compromise. If an admin key is phished or a governance vote is bought, the contract executes exactly as written. No code review prevents that.
- Novel attack classes. Auditors look for what is known. Genuinely new techniques get found in production, which is what a bug bounty is for.
- Off-chain infrastructure. The frontend, the API, the deployment pipeline, and the key management setup are all part of the real attack surface and usually outside audit scope.
An audit is one control in a system of controls. Treat a clean report as evidence of diligence, not as a guarantee of safety, and be suspicious of any firm that presents it as the latter.
Why Must Smart Contract Audits Continue After Deployment?
Because the code stops changing and everything around it does not. New vulnerability classes get discovered, dependencies upgrade, Layer 2 fee models shift incentives, and attackers keep probing. Post-deployment security rests on four mechanisms: circuit breakers, live monitoring, a defined upgrade path, and a bug bounty.
- Pause Functions and Circuit Breakers: A pause mechanism lets you halt contract execution when something looks wrong, which converts a total drain into a contained incident. Design considerations matter here: who can trigger it, how fast, and what happens to in-flight transactions. A pause controlled by a single key is itself a centralization risk, so most teams put it behind a multisig with a small trusted quorum. Rate limits and withdrawal caps do similar work without needing anyone to be awake.
- On-Chain Monitoring and Alerting: Real-time dashboards, automated alerts, and clear escalation paths are standard. Monitor for large unexpected balance changes, privileged function calls, oracle price deviation beyond a threshold, and gas anomalies. The gap between reacting in minutes and reacting in hours is usually the gap between a partial loss and a total one.
- A Defined Upgrade Path: OWASP added proxy and upgradeability vulnerabilities to its 2026 Top 10 as SC10, which tells you how often this goes wrong. If you use a proxy pattern, the upgrade mechanism needs auditing as carefully as the logic it upgrades: storage layout compatibility, implementation initialization, and admin key custody. If you choose immutability instead, that is a valid decision, but it means your only response to a discovered flaw is migration, so plan the migration before you need it. Teams building blockchain app development projects should settle this question at the architecture stage, not after launch.
- A Bug Bounty Program: An audit is finite. A bounty is continuous. Programs on platforms like Immunefi give researchers a legal, paid route to report what they find instead of exploiting it, and the payout is almost always cheaper than the alternative. Size the maximum reward relative to value at risk. A bounty capped at $5,000 on a protocol holding $50 million is not an incentive, it is an insult, and researchers treat it that way.
Teams also need to stay current. New EIPs change assumptions, Layer 2 upgrades shift gas economics, and cross-chain bridges keep opening new surfaces. Ignoring that drift is how audited contracts still get exploited.
How Is Regulation Shaping Smart Contract Audits in 2026?
Regulation is no longer theoretical. MiCA is fully active in Europe and DeFi protocols operating there are expected to maintain audit documentation. In the US, tokenized securities and on-chain financial products are moving toward standardized audit disclosure. Audit records have become part of the compliance file, not just the engineering file.
The persistent challenge is cross-border compliance. Blockchains are global, regulators are not, and that gap creates friction around AML, data privacy, and legal accountability. Specialized audit services have become necessary rather than optional for teams operating at scale.
What has improved is coordination. Regulators, auditors, and industry bodies are converging on shared standards, and third-party audits now function as both a legal requirement and a credibility signal that users, partners, and institutions actively check. Any enterprise engaging a blockchain development company for a regulated deployment should expect audit documentation to be a contractual deliverable.
Conclusion
A smart contract audit is not a final checkbox before deployment. It is a decision-making filter that determines whether your protocol is resilient or fragile from day one. Most costly failures in Web3 are not exotic attack vectors. They are known issues that were underestimated, postponed, or ignored during design and review.
This checklist exists to move that scrutiny earlier in the lifecycle, while assumptions can still be challenged, scope can still be reduced, and risk can still be priced correctly. Teams that use audits as a strategic control point rather than a reactive safety net consistently ship faster, spend less on remediation, and keep credibility with users, partners, and regulators.
If you can answer every item here with confidence, you are ready to deploy with intent. If you cannot, that gap is not a weakness. It is a list of mistakes you still have time to prevent cheaply.
In smart contracts, security is not what you add at the end. It is what you decide at the beginning.
FAQs
Shipra Garg is a tech-focused content strategist and copywriter specializing in Web3, blockchain, and artificial intelligence. She has worked with startups and enterprise teams to craft high-conversion content that bridges deep tech with business impact. Her work translates complex innovations into clear, credible, and engaging narratives that drive growth and build trust in emerging tech markets.