

Key Takeaways
- Document review, risk detection, regulatory reporting: generative AI takes over the grind work, so your team spends less time copy-checking and makes fewer mistakes doing it.
- Monitoring stops being a quarterly exercise. Compliance activity gets watched as it happens, so risks surface early and rule changes do not catch you flat-footed.
- The architecture matters as much as the model. Data pipelines, LLMs, and an integration layer have to work together, or compliance operations will not scale safely.
- Lower cost, faster turnaround, better calls at the decision point. Compliance stops being a fire drill and starts running ahead of the problem.
- Organizations that move early get consistency and scale, plus a head start on whatever the regulators publish next.
Regulatory compliance keeps getting harder. Laws shift, borders multiply the rulebooks you answer to, and the volume of data under review climbs every quarter. Most compliance systems were built to react, and built around people reading documents by hand. That combination gets expensive fast, and it leaves gaps.
But there is another way to run it. With generative AI development solutions handling document analysis, reporting, and risk detection, compliance stops chasing problems after the fact and starts working off signals as they appear.
This piece walks through the use cases that actually earn their keep, the architecture sitting underneath them, and what the shift does to the business. The goal: enough detail to build something that still works two regulations from now.
What is Generative AI for Regulatory Compliance?
Generative AI for regulatory compliance means putting AI models to work on the content and the process itself: reading it, analyzing it, writing it. The payoff is meeting legal and regulatory obligations faster, with fewer slips and less variation between one reviewer and the next.
Around 23% of organizations are actively scaling AI agent systems, which matters here because compliance workflows and the decisions inside them are exactly what those agents automate. Swap out the manual review and the static rules engine, and generative AI can:
- Understand complex regulations
- Analyze large volumes of documents
- Generate reports, summaries, and alerts
- Identify risks or non-compliance in real time
The Role Of Generative AI in Regulatory Compliance
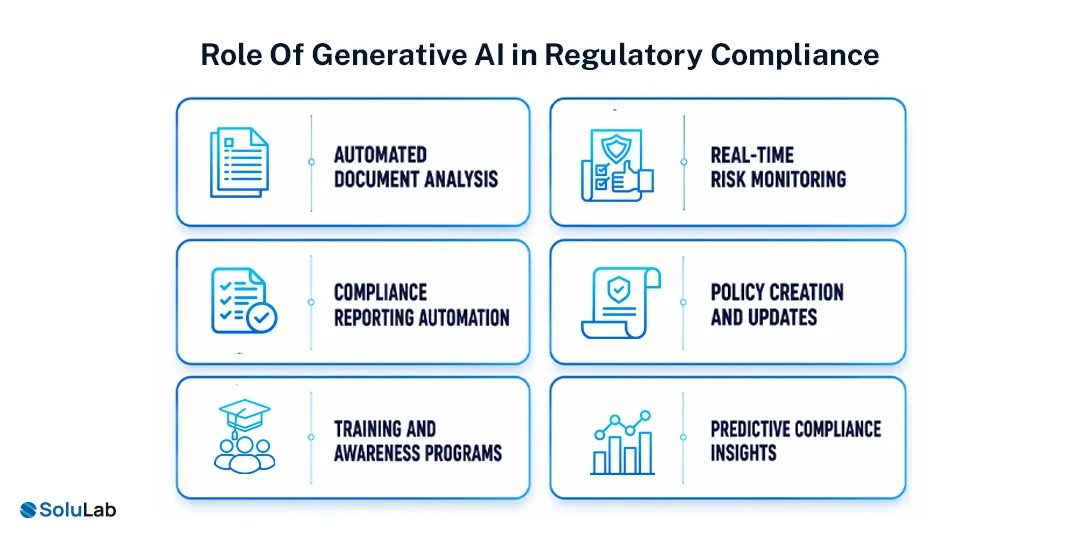
Generative AI integration is rewriting how compliance runs day to day. Messy processes get automated, accuracy climbs, monitoring happens live instead of in retrospect. Teams stay compliant with less manual labor, less operational exposure, and a smaller regulatory bill.
- Automated document analysis: Regulatory texts, contracts, internal policies, all of it goes through the model. Key points come out, alignment with current requirements gets checked, and the hours your team used to spend reading line by line drop sharply. So do the misses.
- Real-time risk monitoring: Transactions, communications, system logs. The model watches them continuously, flags what looks off, and surfaces compliance risk while it is still small rather than after it has become a violation or a fine.
- Compliance reporting automation: Structured tables and unstructured notes both feed in; clean, audit-ready documentation comes out. Filings land on time, and nobody spends a week assembling the same report they assembled last quarter.
- Policy creation and updates: The model reads regulatory changes against your internal data and drafts the revision. Your policies keep pace with the law without someone manually rewriting them every time a rule moves.
- Training and awareness programs: AI development turns dry policy into scenario-based modules built for the specific role taking them. People actually understand what they are being asked to follow, and accidental breaches go down.
- Predictive compliance insights: Feed it history and trend data, and generative AI points at where the trouble is likely to show up next. That lets you act early, put people where they are needed, and run risk management with some foresight behind it.
Benefits of Using Generative AI for Regulatory Compliance
Across sectors, the gains from applying generative AI to compliance tend to show up in a few predictable places:
- Efficiency and Automation: Drafting documents, watching for breaches, chasing sign-offs. Generative AI absorbs a good chunk of that routine regulatory work, and the time compliance management eats up shrinks accordingly.
Read Our Blog: Generative AI and Automation
- Accuracy and Consistency: A model applies the same standard on a Friday afternoon that it applied on Monday morning. Compliance paperwork and procedures come out uniform, and the small contradictions that creep into hand-built documents mostly disappear.
- Real-time Monitoring and Cautionary Notes: Data and transactions stay under continuous watch. When something breaches a rule, the alert fires immediately, and you can fix it while it is still a small problem.
- Predictive Analytics for Risk Mitigation: Historical data holds patterns. AI reads them, points at compliance risks forming ahead of you, and gives the company room to deal with a concern long before it turns into a real problem.
How To Implement Generative AI Solutions In Regulatory Compliance?
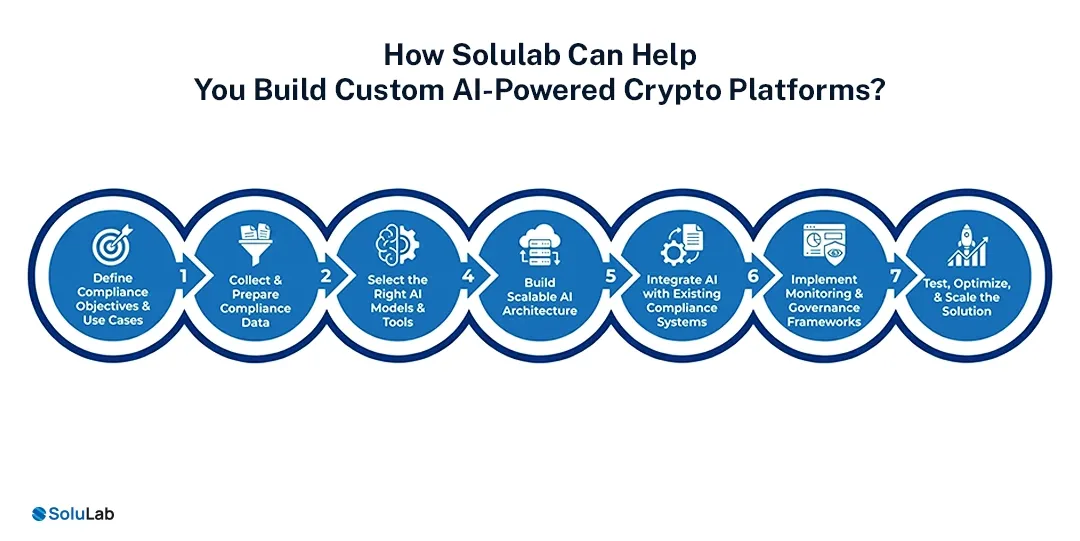
Generative AI solutions are already improving how compliance gets done: tangled processes automated, accuracy up, monitoring happening in real time. Risk drops, adherence holds, and compliance operations scale without adding headcount in proportion. Kavach, a regulatory compliance platform we built for banks, is one example of this sequence working end to end. Here is the sequence that tends to work.
Step 1. Define Compliance Objectives and Use Cases
Start with the pain. Is it document analysis, weak risk detection, or reporting that takes three weeks it should not take? Name the gap first, then match generative AI use cases to it. Skip this step and you end up with a pilot nobody uses.
Step 2. Collect and Prepare Compliance Data
Pull in everything: policies, contracts, regulatory filings, structured records and loose documents alike. Then clean it, sort it, and get it into a consistent shape. This is the unglamorous part, and it is the part that decides whether the model’s output is trustworthy.
Step 3. Select the Right AI Models and Tools
Pick models that fit the job, not the ones with the best press. LLMs and NLP systems both have a place here; what matters is whether they handle the text generation, classification, summarization, and monitoring your use case actually calls for.
Step 4. Build Scalable AI Architecture
APIs, cloud platforms, microservices. Put together an infrastructure that holds up under load, talks cleanly to the rest of the stack, processes in real time, and grows with the compliance workflows running on top of it. AI-led development eases the whole concept with speed and flawless execution.
Step 5. Integrate AI with Existing Compliance Systems
Wire the AI into what you already run: the legacy tools, the CRM, the compliance platform your team lives in. Data should move between them without friction, and the existing process should keep working while you do it. In practice, this is where most projects stall.
Step 6. Implement Monitoring and Governance Frameworks
Build the audit trail before you need it. Monitoring systems, logged decisions, governance rules that spell out who answers for what. You want to be able to show a regulator why the model said what it said, and you want bias or plain inaccuracy caught internally first.
Step 7. Test, Optimize, and Scale the Solution
Keep measuring. Take the feedback from the people using it, tune the outputs, and only then push AI deployment out to other departments. Scaling something half-tuned just multiplies the flaws.
Generative AI Applications in Compliance
Because generative AI builds new content out of the patterns it learns from your data, it slots into compliance work in more places than most teams expect. A few of the clearest:
1. Automated Document Generation: Policies, procedures, contracts, regulatory reports. Generative AI reads your existing templates alongside the relevant regulations and your own organizational data, then writes the document to match the requirement in front of it. What used to be a week of drafting becomes a review pass.
2. Natural Language Generation (NLG) for Regulatory Reporting: NLG systems take structured data and turn it into prose a person can read. The output covers key metrics, where compliance currently stands, and what the risk assessment found, which makes the conversation with stakeholders and regulators a lot less painful.
3. Compliance Training and Simulation: Interactive modules and simulations, generated rather than hand-built, covering policy, procedure, and the ethical grey areas. The AI writes scenarios that mirror real compliance dilemmas, so employees practice the judgment call somewhere the wrong answer costs nothing.
4. AI-Powered Compliance Monitoring: Feed the algorithms enough data and they will watch adherence to regulations, internal policy, and your control environment continuously. Patterns emerge, anomalies stand out, behavior that deviates from the norm gets flagged. Fraud, insider trading, data privacy breaches: these are the areas where that early flag is worth the most.
5. Regulatory Compliance Audits: During an audit, generative AI works through documents, transactions, and operational records against the regulatory requirement. Discrepancies, contradictions, and gaps in compliance come out automatically. The audit moves faster, and far less gets missed because someone was on page 400 at 9pm.
6. Contract Analysis and Due Diligence: natural language processing (NLP) tools built on generative AI read legal contracts, agreements, and regulatory documents to find the clauses that matter, the obligations buried in them, and the compliance risk attached. Key terms get extracted, questionable language gets flagged, and the output feeds straight into due diligence and AI contract management processes.
7. Predictive Analytics for Compliance Risk Management: Your compliance history is a dataset. Generative AI mines it for trends, repeat patterns, and risks that are beginning to form. Apply predictive techniques on top and you get a forecast of where the next issue lands, which changes how you allocate people and how early you can act.
8. AI-Driven Regulatory Compliance Chatbots: Generative AI-powered chatbots can answer compliance questions the moment someone asks. Ask it in plain language, it pulls the relevant compliance information and responds to your situation specifically. Employees, customers, anyone who needs an answer gets one without filing a ticket and waiting two days.
Related: Effective Generative AI Strategy For Your Enterprise
Future of GenAI in Regulatory Compliance
Where is this heading? Generative AI trends in regulatory compliance point toward systems that run themselves: managing risk before it lands, holding adherence in real time, and cutting the manual load while accuracy and scale both improve.
- Autonomous compliance systems: AI stops being the assistant. It tracks regulations on its own, spots the risk, and corrects the course in real time. Less human oversight needed, more throughput out the other end.
- Real-time regulatory adaptation: Rules change in one jurisdiction and the system notices. Policies and workflows update themselves, so compliance holds without a lag and without someone manually pushing the change through.
- Predictive risk intelligence: AI models will read historical and live data together to call compliance risks before they materialize. That is the difference between paying a penalty and never triggering one.
- Hyper-personalized compliance frameworks: AI native strategy will shape the compliance strategy around your industry, your geography, and how your business actually operates, which makes it far more workable inside a complicated organization.
- AI-driven audit and reporting automation: Documentation, reporting, audit prep. All of it automated, all of it current, with the administrative pile and the human errors on top of it both shrinking.
Conclusion
The shift underway is from a function that reacts to one that anticipates. Document review handled automatically, risk caught as it happens, regulatory reports that assemble themselves: the effect shows up in speed, in accuracy, and in how far the same compliance team can stretch.
Companies building AI-driven compliance architectures carry less operational overhead and less regulatory exposure than the ones still doing it by hand. And the requirements are not going to get simpler. Generative AI has moved from an experiment worth running to infrastructure worth owning.
Building one from scratch, or scaling what you already have? SoluLab, a generative AI consulting company, can help you design and deploy something that fits your actual regulatory footprint.
FAQs
Neha is a curious content writer with a knack for breaking down complex technologies into meaningful, reader-friendly insights. With experience in blockchain, digital assets, and enterprise tech, she focuses on creating content that informs, connects, and supports strategic decision-making.