

Key Takeaways
- The problem: Teams are shipping AI faster than they are governing it. Nobody owns the model, nobody can explain the output, nobody checked the training data. Then bias shows up, an auditor asks a question, a security gap opens, and trust with users and regulators quietly drains away.
- The solution: AI TRiSM gives you a structure for trust, risk, and security that spans the whole AI lifecycle. Transparent systems. Compliant systems. Monitored continuously, with a named owner for every model.
- How SoluLab helps: We are an AI-native company, so TRiSM principles sit inside our build process rather than bolted on at the end. Using AI on our own workflows is what keeps delivery fast and costs sane, while security, scale, and responsible deployment stay non-negotiable.
Every industry is buying AI right now. Very few of them trust it yet, and that gap is what stops pilots from becoming production. As organizations prefer AI integration solutions for their workflows, the awkward questions about bias, security, compliance, and transparency stop being theoretical and start landing on someone’s desk.
AI TRiSM (Trust, Risk, and Security Management) is the answer a lot of governance teams have settled on. It is a framework for keeping AI systems reliable, explainable, and defensible in front of a regulator.
The core idea is simple. Trust is not a phase you add after launch; it gets wired into every stage of the lifecycle. Budgets are already moving that way: around 64% of organizations are increasing their spending on AI governance tools, and over 54% are boosting their investments in data security.
Data governance, model monitoring, risk control. Put those three together and you get AI that stakeholders will actually sign off on, with far less exposure on the operational, ethical, and legal side.
What is AI TRiSM?
AI TRiSM (AI Trust, Risk, and Security Management) is a framework for keeping your AI systems reliable, secure, compliant, and ethically defensible across their entire lifecycle, not just on launch day.
Its job is to manage risk and build trust in the decisions your models make, which matters more every month as AI native strategy works its way deeper into day-to-day operations.
Here’s what it covers:
- Trust in AI systems: Models that produce accurate, explainable, consistent output. No hidden behavior, no shrugging when someone asks why the system said no.
- Risk management: Catching model drift, wrong predictions, data leakage, and the odd outcome nobody designed for, before any of it dents business performance.
- Security protection: Defence against data poisoning, adversarial inputs, and unauthorized access, all of which can quietly corrupt model integrity and the outputs people act on.
- Compliance and governance: Lining AI usage up with regulation and internal policy, so transparency, auditability, and responsible practice hold across every deployment you run.
Why AI TRiSM Matters Now?
AI TRiSM has moved from nice-to-have to necessary as enterprise AI adoption, bringing trust, risk control, and governance to decision systems that are getting more automated and more tangled by the quarter, and heading off failures, bias, and compliance trouble before they surface.
- Rising regulatory pressure: Governments keep tightening AI governance rules. That pushes organizations toward real transparency, accountability, and auditability, because the alternative is legal exposure, fines, and a deployment you have to switch off.
- Increased model complexity: Today’s systems are large and interconnected, and interpreting them is genuinely hard. TRiSM frameworks are how you watch behavior, spot anomalies, and keep the thing reliable.
- Bias and ethical risks: Imperfect training data produces unfair outcomes. TRiSM keeps fairness under continuous assessment so discrimination gets caught, and your brand and your users’ trust survive.
- Enterprise-wide AI adoption: Every new department running AI multiplies unmanaged risk. Central governance, one consistent policy set, and real-time monitoring are what keep that sprawl safe and scalable.
How does AI TRiSM work?
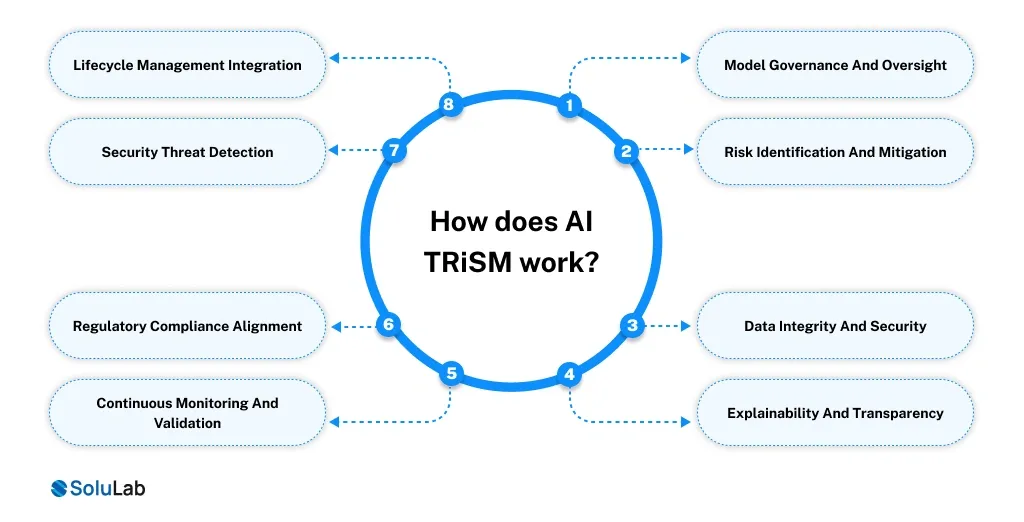
Mechanically, AI TRiSM works by watching. Models, data, and decisions stay under continuous observation across the lifecycle, which is how risk gets kept down and compliance gets kept intact while the system runs reliably, securely, and within ethical limits.
- Model governance and oversight: Policies, roles, accountability. Write them down, assign them, and every model gets built, deployed, and maintained under the same oversight instead of whatever the team improvised that sprint.
- Risk identification and mitigation: Bias, drift, and adversarial attacks get detected on an ongoing basis, then countered, so accuracy, fairness, and resilience hold up once the model meets messy real-world input.
- Data integrity and security: Sources get validated, access gets controlled, pipelines get watched. Tampering, leakage, and poisoning are all ways a model quietly stops being trustworthy.
- Explainability and transparency: Interpretable models plus audit trails mean stakeholders can follow how a decision got made. In regulated or high-stakes use, that is the difference between accountability and a guess.
- Continuous monitoring and validation: Performance, anomalies, and compliance breaches are tracked live. Something slips, you correct it the same day rather than the next audit cycle.
- Regulatory compliance alignment: Legal and ethical standards keep moving, and TRiSM keeps systems aligned with data protection law, industry regulation, and internal governance across whichever regions you operate in.
- Security threat detection: Model theft, inference attacks, manipulation attempts. These get found early and fenced off, protecting both the models and the infrastructure they sit on.
- Lifecycle management integration: Trust, risk, and security practices run from development through deployment and into retraining, which is what keeps governance consistent and the system sound over years rather than weeks.
The 4 Pillars of AI TRiSM
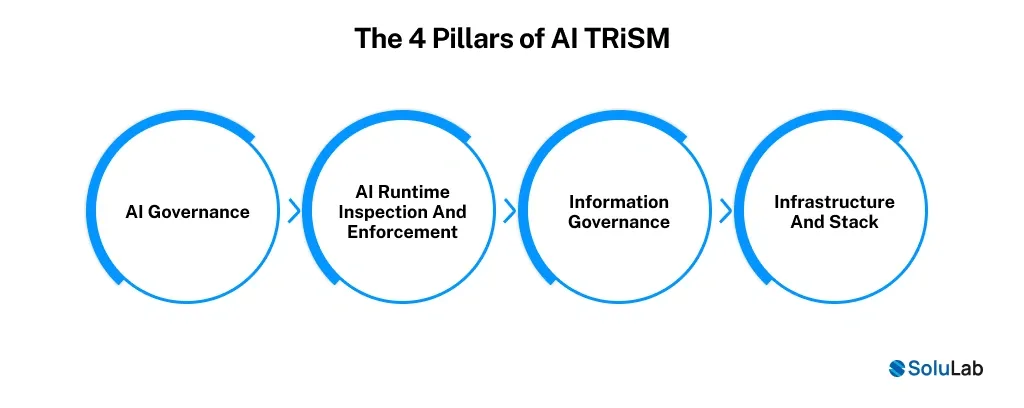
AI scales fast. Risk scales with it, and without guardrails it usually gets there first. AI TRiSM gives you a structured way to put trust, control, and accountability into a deployment while it is still small enough to fix.
1. AI Governance
Start here. Governance sets out how AI gets designed, approved, and watched across the organization. Skip it and your AI estate turns inconsistent and risky within a couple of quarters.
- Write clear policies covering AI usage, development, and deployment
- Name the roles, the owners, and who answers for what across teams
- Keep everything lined up with legal, ethical, and regulatory requirements
- Create audit trails for decisions made by AI systems
2. AI Runtime Inspection and Enforcement
This pillar is about life after deployment, where the model meets conditions nobody simulated. Does it still behave the way you expected?
- Watch model outputs continuously for anomalies or bias
- Enforce rules in real time to stop harmful or non-compliant behavior
- Catch drift in data or model performance early
- Fire alerts or automated interventions the moment risk appears
3. Information Governance
A model is only as good as what you feed it. This pillar keeps the data accurate, secure, and compliant, which is unglamorous work and also where most failures start.
- Hold data quality, consistency, and lineage steady across systems
- Put access controls and privacy safeguards in place
- Stay compliant with data protection regulations
- Track how data is used and transformed inside AI workflows
4. Infrastructure and Stack
Everything above rests on this. Get the technical foundation right and scalability, security, and performance follow.
- Build secure, scalable environments for AI development and deployment
- Wire in tools for monitoring, logging, and model management
- Standardize platforms so fragmentation and risk stop compounding
- Make updates, testing, and rollback painless
Benefits of Implementing AI TRiSM Principles
Put TRiSM principles to work and you end up with AI that is reliable, compliant, and secure, adopted responsibly instead of hopefully, with a lot less operational, ethical, and regulatory risk hanging over it.
- Improved AI Trust: Transparency, explainability, and accountability improve together. Stakeholders can see why a decision went the way it did, and confidence in the output rises where it counts most, in the applications your business actually depends on.
- Enhanced Regulatory Compliance: Governance, auditability, and documentation line up with regulation as it evolves, which cuts the odds of penalties and the kind of compliance scramble that stalls a roadmap for a month.
- Reduced Risk: Find the biases, vulnerabilities, and security gaps early and the operational, reputational, and ethical exposure shrinks. Deployment gets safer, and the solution is still standing in three years.
How to Get Started with Implementing AI TRiSM?
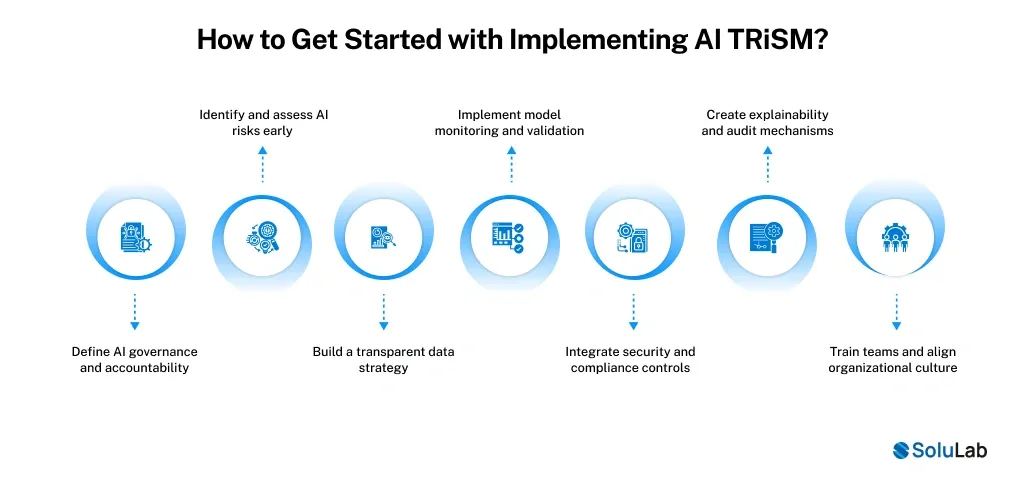
Deploying AI responsibly means governance, compliance, fairness, and security show up at every stage from design through deployment. That is what AI TRiSM (Trust, Risk, and Security Management) is for. Here is the order that tends to work.
1. Define AI governance and accountability
With an expert AI consulting service provider, set up a governance framework that spells out ownership, roles, and who has decision-making authority over AI systems. Accountability needs to be explicit across teams, otherwise responsible usage, compliance, and oversight all quietly become nobody’s job.
2. Identify and assess AI risks early
Run structured risk assessments. Bias, data privacy, security holes, regulatory exposure: name them while the design is still on a whiteboard. Controls you design early cost a fraction of the ones you retrofit after something breaks in production.
3. Build a transparent data strategy
The data behind your models has to be high quality, traceable, and legal. Document sources, lineage, and usage policy properly. Explainability, auditability, and ethical implementation all depend on paperwork nobody enjoys writing.
4. Implement model monitoring and validation
Models drift. Watch for performance decay, bias, and behavior you did not expect, and put validation processes and feedback loops around them so accuracy and fairness hold against business and regulatory expectations over time.
5. Integrate security and compliance controls
Access control, encryption, threat detection: build these into the AI system rather than around it. Line the implementation up with the regulatory standards that apply to you, and sensitive data stays protected against both misuse and breach.
6. Create explainability and audit mechanisms
Make decisions traceable. Log model behavior, keep audit trails, give stakeholders a way to review outcomes themselves. In practice, this is the step that turns a regulator conversation from tense into routine.
7. Train teams and align organizational culture
Give your people the knowledge and tooling to implement AI responsibly, or hire AI experts who are well aware of all this. Culture does the rest: ethical use as a default, cross-functional collaboration, and the habit of improving the framework instead of letting it go stale.
AI TRiSM Major Use Cases and Examples
Any enterprise running AI at scale has to manage and mitigate risk somehow, and TRiSM frameworks are how most of them do it. Below are the sectors leaning on the framework hardest, plus an AI TRiSM example that makes the shape of it clearer:
Case Study For Example
The Danish Business Authority wanted its AI models to be accountable, transparent, and above all fair. So the DBA did something fairly unusual: it took the organization’s ethical standards and wired them directly into its algorithms. Abstract values got tied to concrete acts, such as:
- Running model results through fairness tests on a regular schedule.
- Settling, up front, on what model monitoring actually means in practice.
Those tactics carried sixteen AI models through deployment and ongoing management, models analyzing financial transactions worth billions of Euros. The payoff was credibility: stakeholders and consumers had a reason to trust the system, and the ethical standing of the models held up under scrutiny.
HealthCare
- Accuracy in Diagnosis: Testing and monitoring never stop under AI TRiSM, which is how AI in healthcare diagnosis tools stay accurate and dependable. Drift and bias are what turn a good diagnostic model into a wrong one, and this is the check against that.
- Managing Patient Data: HIPAA compliance, private patient information kept private, and patients who feel safer for it. The TRiSM framework covers all three.
Banking and Financial Services
- Regulatory Compliance: Financial firms mostly reach for AI TRiSM on the compliance side, because requirements like the Fair Credit Reporting Act and the GDPR keep shifting under them. Automating the risk assessment procedures is how they keep pace.
- Detection of Fraud Activities: Fraud detection has to be both extremely accurate and ethically sound, and that combination is exactly what the AI TRiSM framework is built to support. Suspicious transactions get flagged,
Institutional
- Adaptable Education Systems: AI TRiSM keeps AI-powered adaptive learning solutions fair and open about how they work, so learning outcomes improve without quietly favouring some students over others.
- Data Security: Students hand over sensitive information. AI TRiSM protects it while meeting the ethical and legal bar for data privacy.
E-Commerce and Retail
- Supply Chain Optimization: Point AI TRiSM at the conversational AI applications running your supply chain logistics and the biases and hazards inside them become visible, which is the only way you get results that are both efficient and fair.
- Personalized Experiences: Personalization is where ethics gets tested fastest. AI TRiSM helps you think through the moral side of it and keeps consumer profiling and data processing inside privacy regulation.
Can AI TRiSM promise Secure and Responsive AI?
AI Trust, Risk, and Security Management is one more way of asking whether responsible AI services are secure, dependable, and genuinely responsive to what users and other interested parties need. Integrating AI TRiSM technology in a given industry is complicated, and as more industries adopt it, the argument for handling risk and security methodically rather than case by case only gets stronger. AI TRiSM use cases come with their own failure modes, so it brings measures that strengthen accountability, reporting, and legal compliance. Here is how the promise of secure, responsive AI actually cashes out:
- Decreased Risks and Enhanced Security: Models are exposed to both bias and cyberattack. AI TRiSM surfaces those threats and reduces them through security procedures and impartial decision-making, which leaves you with safer, more dependable models and a company that is harder to damage.
- Gaining Stakeholders’ Trust: Trust starts with transparency. AI TRiSM pushes toward explainable AI, models that can state precisely why they chose what they chose. Once consumers, employees, and regulators accept that, the organization uses AI with far more confidence.
- Maximized Business Value: Build ethically and you get to use the technology fully. Data protection and compliance are assured under AI TRiSM, which means sensitive data becomes usable rather than off-limits, and decision-making, efficiency, and customer experience all improve as a result.
The Future of AI TRiSM
Right now TRiSM is mostly a compliance obligation. That is changing. As AI adoption spreads across industries, trust, risk monitoring, and governance will get designed in from the first architecture review rather than argued about after launch.
AI systems in businesses will become more transparent, more self-auditing, and better aligned with global regulatory standards. Real-time risk detection, automated compliance checks, continuous model monitoring: that is what the next generation of AI operations looks like.
Embed TRiSM early and you get a genuine edge, because your AI is reliable, ethical, and able to scale. Ignore it and you inherit the opposite: trust gaps, regulatory pressure, and vulnerabilities you find out about at the worst possible moment.
How SoluLab Helps Implement AI TRiSM at Scale?
Building AI is rarely the hard part anymore. Making it reliable, explainable, and safe once it is serving real traffic, that is the hard part. That’s where SoluLab fits in.
We treat AI TRiSM as part of the AI led development lifecycle rather than a compliance pass at the end. Governance layers, risk checkpoints, and data validation pipelines get defined during initial architecture, so trust is structural from day one.
Monitoring goes in at design time too. Teams can watch model behavior, catch drift, and spot bias before a real user ever feels it. Long-term operational risk drops, and performance stops drifting sideways six months in.
Security and compliance run alongside AI-led development, not behind it. Access controls, audit trails, and regulatory alignment land early, which is how you avoid the rework bill later.
Explore our successful projects, such as the AI-Based Financial Recommendation System and Cyberhulk.
One more thing worth knowing about how we work. SoluLab is AI-native internally, so we run AI across our own workflows to compress development cycles, hold costs down, and ship faster without letting quality slip. Partner with us today!
Conclusion
Once AI starts running operations you cannot afford to get wrong, TRiSM stops being optional. It puts structure around trust, risk, and security, and it keeps compliance and ethical usage from being an afterthought.
Governance, monitoring, and transparency built into the system are what turn uncertainty into confidence, for your users, your regulators, and everyone else with a stake in the outcome. SoluLab, an AI development company, can help your business implement AI TRiSM effectively and scale AI with confidence.
FAQs
Shipra Garg is a tech-focused content strategist and copywriter specializing in Web3, blockchain, and artificial intelligence. She has worked with startups and enterprise teams to craft high-conversion content that bridges deep tech with business impact. Her work translates complex innovations into clear, credible, and engaging narratives that drive growth and build trust in emerging tech markets.